|
1825 Monetary Lane Suite #104 Carrollton, TX
Do a presentation at NTLUG.
What is the Linux Installation Project?
Real companies using Linux!
Not just for business anymore.
Providing ready to run platforms on Linux
|
Show Descriptions... (Show All/All+Images)
(Single Column)
- Glasswing overwhelms maintainers with underwhelming findings (VulnCheck)
Patrick Garrity of VulnCheck has written a blogpost that looks at vulnerabilities found by Anthropic's Project Glasswing since itlaunched on April 7, and finds it wanting:
Of the 37,966 findings Anthropic reports, only 7,349 (19.4%) have been madepublic. Just 217 of those have been marked fixed. The more glaring number isthat 4.4% (1,654) of the project's findings have already been marked asduplicates, 7.5x more duplicates than fixes. On top of that, 419 findings havebeen withdrawn. It seems odd that the ledger now claims a 94.2% true positiverate, up from 90.8% at launch, when more findings have been withdrawn or markedas duplicates than fixed, likely a feedback loop missing to the triage rateslisted as "True Positives".
[...] AI is a valuable tool for finding vulnerabilities, and I'm notdiscounting that. But seven months in, the evidence still doesn't match thelaunch narrative. The CVEs are a sliver of this year's total, almost none arebeing exploited, fixes have stalled while duplicates and withdrawals pile up,and the triage burden is shifting onto the open source maintainers Glasswingpromised to help. The receipts keep coming in. They still don't reconcile.
- Introducing Polo: a Wayland MATE compositor
Kerem Söke has announcedthe 1.0release of Polo, aWayland compositor for the MATE DesktopEnvironment:
The idea is to keep MATE behaving as closely as possible to how it does onX11, rather than changing the desktop to fit a different compositor. [...]
Window management, metacity, workspaces, tiling, XWayland, clipboard andclipman support, multiple monitors, display scaling, hotplugging, screenshots,screen sharing, and session management are all working.
I've also added desktop effects: fade, zoom, zap, spin, squeemize, magiclamp, desktop cube, expo, and wobbly windows.
Söke is looking for people to test Polo, particularly on multi-monitorsetups, and report back with problems.
- [$] C++26 contract confusion
TheInternational Organization for Standardization (ISO) has blessed seven C++language revisions since 1998.The language is mostly developed by ISO'sWorking Group 21, whichconsiders proposed additions and amendments, integrates them into a document,and then presents that document to the main ISO body to be voted on as astandard. On October 23, for the first time ever, ISO declined to ratify a documentpresented by Working Group 21, leaving the future of the C++26 standard indoubt. The decision was driven by controversy around a proposed new "contracts"feature that would add pre- and post-conditions to function signatures.
- Stenberg: 30 years of Internet transfers with curl
Daniel Stenberg reflectson the 30th anniversary of the curl project.
libcurl runs in an estimated thirty billion installations today. It is a rough estimate since the majority of all libcurl users never tell us they use it, but we need to find it mentioned in their credit screens, open source license windows or their manuals. A super popular app might use libcurl today and not tomorrow, or vice versa, which can make the numbers shift by several billions overnight. In reality of course, once the pulse raise has calmed down and your ego is content, these numbers do not matter. In our corner of the world, things don't change notably when we go from a thousand installs to billions. We still work with similar people, in similar ways, with similar challenges.
- Security updates for Thursday
Security updates have been issued by Debian (aodh, apache2, dnspython, firefox-esr, mutt, octavia, spip, thunderbird, and watcher), Fedora (epiphany, firefox, freerdp, java-25-openjdk, java-latest-openjdk, libsoup3, perl-HTTP-Parser-XS, perl-libnet, php-getid3, pipx, python-crate-ingredients, python-pillow, python-robotframework, python3.9, rsync, rubygem-nokogiri, tpm2-tss, udns, and xorg-x11-server-Xwayland), Gentoo (curl, ImageMagick, libheif, and PCRE2), Mageia (nginx and python-django), Oracle (go-toolset:rhel8, libimobiledevice, nodejs:22, util-linux, and vim), Red Hat (.NET 10.0, .NET 8.0, .NET 9.0, cockpit, freerdp, gdb, go-fdo-client, grafana-pcp, ignition, kernel, kernel-rt, krb5, openssh, openssl, osbuild-composer, rpm, rsync, and webkit2gtk3), Slackware (git, httpd, and tigervnc), SUSE (aliyun-cli, alloy, apache-parent, aqute-bnd, google-gson, logback, maven, maven-artifact-transfer, maven-parent, maven-resolver, methanol, osgi-service- subsystem, slf4j, xmvn, bcel, benchdnn, containerd, distribution, dpdk, efivar, elemental, elemental-register, elemental-system-agent, elemental-toolkit, firefox, kernel, liblldpctl4, libonnxruntime1, openssl-1_0_0, openssl-1_1, openvpn, pcre2, perl-Net-DNS, perl-Plack, perl-Starman, psqlODBC, python-M2Crypto, python-Pillow, python-Twisted, python-urllib3_1, python313-djangorestframework, python313-fpdf2, python313-langgraph-sdk, python313-nltk, rust-keylime, skopeo, traefik, zchunk, and zvbi), and Ubuntu (asyncpg, awl, btrbk, davical, dotnet8, dotnet10, dotnet11, libfcgi, linux-raspi, logback, mysql-8.0, mysql-8.4, mysql-9.7, network-manager-ssh, node-babel, php-pecl-http, prosody-modules, rkhunter, ruby-actionpack-page-caching, ruby-jwt, ruby-kramdown, shiro, snmptt, and yodl).
- [$] LWN.net Weekly Edition for November 12, 2026
Inside this week's LWN.net Weekly Edition:
Front: Synaptics patent claims; Git LLM policy; Hibernation and lockdown; User namespaces; glibc tunables. Briefs: *sshole; Amutable foundations; Asahi Linux 7.3; OpenIndiana 2026.10; Firefox 160; Quotes; ... Announcements: Newsletters, conferences, security updates, patches, and more.
- Zellij 0.46 released
Version0.46 of the Zellij terminal workspace hasbeen released.
This release includes a major addition in Zellij: Zellij is now also adesktop terminal. To run it: zellij terminal. It works on linux, mac andwindows.
Nothing changes for the normal multiplexer - Zellij can still run insideanother terminal. Both sessions are the same and can be shared.
Additional features in this release include aGUI settings screen, session previews, and right-click menu. See this walkthroughfor more on the 0.46 release.
- In Memoriam: Tim Peters 1952–2026
Guido van Rossum conveysthe sad (and somewhat delayed) news of the passing of Tim Peters.
It's hard to overestimate Tim's influence on Python. He's probably best known for writing the Zen of Python (PEP 20), but to me he was a mentor and language co-designer long before that.
Tim found Python not long after its initial release. His first deed was to convince me that Python should support mixed arithmetic between int and float, because most users would expect them to work that way. And he never stopped contributing.
- Security updates for Wednesday
Security updates have been issued by AlmaLinux (edk2), Debian (openexr, rsyslog, and srt), Fedora (alertmanager, dotnet11.0, gdal, mstflint, nextcloud, python-crate-ingredients, rust-ingredients, rust-pore, rust-pulldown-cmark, rust-rbw, rust-sequoia-sq, rust-siguldry-fedora-autopen, tigervnc, unbound, and zchunk), Gentoo (Brotli, git, and libde265), Mageia (mopidy, python-dulwich, rust-similar3, rclone, and sofia-sip), Oracle (dpdk, edk2, firefox, glibc, kernel, kernel-uek, nodejs-nodemon, nodejs22, nodejs:24, patch, ruby, ruby4.0, squid:4, and thunderbird), Red Hat (.NET 10.0, .NET 11.0, .NET 8.0, .NET 9.0, bind, bind9.16, bind9.18, buildah, c-ares, containernetworking-plugins, delve, flatpak-builder, gcc, gcc-toolset-15-gcc, gcc-toolset-16-gcc, go-fdo-client, go-fdo-server, golang-github-openprinting-ipp-usb, grafana, grafana-pcp, gstreamer1-plugins-bad-free, gstreamer1-plugins-good, gvfs, gvisor-tap-vsock, nginx, nginx:1.24, nginx:1.26, oci-delta, podman, python-oauthlib, python3, python3.12, python3.9, qt5-qtbase, qt6-qtbase, rhc, runc, skopeo, squid, squid:4, tesseract, util-linux, xdg-dbus-proxy, and yggdrasil), Slackware (xorg-server), SUSE (aliyun-cli, amazon-cloudwatch-agent, ansible-core, aspell, azure-storage-azcopy, bind, cups, dlib-devel, docker, dolphin, dpdk, evolution, firefox, flannel, fuse-overlayfs, gnome-podcasts, google-cloud-sap-agent, GraphicsMagick, graphicsmagick, haproxy, istioctl, kernel, kubevirt, kured, libvips-devel, libXi, mozilla-nss, nvidia-open-driver-G06-signed-check, okteto, openssl-1_1, pcre2, poppler, poppler-qt, poppler-qt5, poppler, poppler-qt5, proftpd, psqlodbc, python-graphql-core, python-M2Crypto, python-pillow, python-soupsieve, python-urllib3_1, python313-wyoming, qt6-coap, rust-keylime, sbc, scribus, SDL2_image, tar, terraform-provider-susepubliccloud, the linux kernel (live patch 18 for suse linux, vsftpd, xen, xorg-x11-server, and zchunk), and Ubuntu (ca-certificates-java, gst-plugins-good1.0, gst-plugins-base1.0, hplip, linux-azure-fde, linux-nvidia, linux-nvidia-7.0, linux-nvidia-bos, linux-nvidia-lowlatency, python-tornado, rust-coreutils, and unbound).
- Three new stable kernels for Tuesday
Greg Kroah-Hartman has released the 7.3.4,6.18.63, and 6.12.117 stable kernels. The 7.3.4 kernel has morethan 1,250 patches, 6.18.63 contains more than 860, and 6.12.117 includes morethan 1,530 patches. Users of these kernels are, of course, encouraged to upgrade.
- [$] Synaptics patent claims stop work on DisplayLink drivers
Mike Lothian owns a docking station (or dock) that uses a DisplayLink chipsetthat had, at least in his opinion, subpar performance on Linux. Hedecided to try improving the Linux driver, with LLM assistance, but ran into oneproblem that he could not solve—so he asked for help, hoping thatSynaptics's developers would lend a hand. (DisplayLink was acquired bySynaptics in 2022.) Rather than help him in improving thedriver, however, the Synaptics legal team responded with patent infringementclaims, a demandthat he cease unauthorized implementation of DisplayLink technology, and threatsof expensive legal penalties. For now, it appears that Linux users of thecompany's docks will have to continue to live without feature parity with otherplatforms.
- Firefox 160 released
Version160 of the Firefox web browser has been released. Notable features in thisrelease include the ability to block sites from asking to handle"mailto:" links, ability to play Matroska files with FLAC, MP3, or PCMaudio, playback speed controls in the picture-in-picturevideo player, and a new MiniWindow feature that is in early development.
- Security updates for Tuesday
Security updates have been issued by AlmaLinux (curl, dpdk, glibc, kernel, nodejs-nodemon, nodejs22, nodejs24, nodejs:18, nodejs:22, patch, qt5, qt5-qtdeclarative, ruby, ruby4.0, ruby:3.3, ruby:4.0, squid:4, tomcat, util-linux, and webkit2gtk3), Debian (symfony and tomcat10), Fedora (bind, dnf5, kernel, kernel-headers, libmodulemd, maturin, perl-CGI, perl-Net-IDN-Encode, perl-Starlet, python-jiter, python-pydantic-core, python-pysequoia, python3-docs, python3.14, python3.15, ruff, rust-afterburn, rust-astral_async_zip, rust-clearscreen, rust-jiter, rust-lzma-rust2, rust-mailparse, rust-pyo3-introspection, rust-python-pkginfo, rust-serde_json, rust-testresult, rust-zip, selenium-manager, ty, and uutils-coreutils), Mageia (glibc, packages, php-smarty, python-aiohttp, and thunderbird), Oracle (curl, firefox, gdb, glibc, kernel, oVirt 4.5 ovirt-engine-wildfly, perl-YAML:1.24, and tesseract), Slackware (krb5), SUSE (ansible-core, apr-util, aspell, buildpacks-cli, dpdk22, firefox, git-bug, glib2, google-cloud-sap-agent, haproxy, jsoup, kernel, krb5, libjxl, librsvg, libruby4_0-4_0, libunbound8, libXtst, nodejs24, nvidia-open-driver-G07-signed, PackageKit, perl-XS-Parse-Keyword, poppler, python, python-Brotli, rsyslog, tekton-cli, tomcat, tomcat10, tomcat11, trivy, udisks2, xen, zchunk, and zk), and Ubuntu (apache2, ca-certificates, fetchmail, freerdp3, kernel, libgphoto2, libheif, libnfs, libsoup3, linux, linux-aws, linux-aws-5.15, linux-aws-fips, linux-azure, linux-azure-5.15, linux-azure-fde-5.15, linux-azure-fips, linux-gcp, linux-gcp-5.15, linux-gcp-fips, linux-gke, linux-gkeop, linux-hwe-5.15, linux-ibm, linux-ibm-5.15, linux-intel-iot-realtime, linux-intel-iotg, linux-intel-iotg-5.15, linux-kvm, linux-lowlatency, linux-lowlatency-hwe-5.15, linux-nvidia, linux-nvidia-tegra, linux-nvidia-tegra-5.15, linux-oracle, linux-oracle-5.15, linux-realtime, linux, linux-aws, linux-aws-fips, linux-aws-hwe, linux-azure, linux-azure-4.15, linux-azure-fips, linux-fips, linux-gcp, linux-gcp-4.15, linux-gcp-fips, linux-hwe, linux-kvm, linux-oracle, linux, linux-aws, linux-aws-fips, linux-azure, linux-azure-5.4, linux-azure-fips, linux-bluefield, linux-fips, linux-gcp, linux-gcp-5.4, linux-gcp-fips, linux-hwe-5.4, linux-ibm, linux-ibm-5.4, linux-iot, linux-kvm, linux-oracle, linux-oracle-5.4, linux-xilinx-zynqmp, linux, linux-aws, linux-azure, linux-azure-fips, linux-gcp, linux-gke, linux-ibm, linux-lowlatency, linux-oracle, linux-vmware, linux, linux-aws, linux-gcp, linux-ibm, linux-oem-7.0, linux-oracle, linux, linux-aws, linux-kvm, linux-lts-xenial, linux-aws, linux-aws-5.4, linux-raspi, linux-raspi-5.4, linux-aws-6.8, linux-gcp-6.8, linux-ibm-6.8, linux-lowlatency-hwe-6.8, linux-nvidia, linux-realtime-6.8, linux-aws-7.0, linux-azure-fde, linux-azure-fde-7.0, linux-gcp-7.0, linux-gke, linux-oracle-7.0, linux-realtime, linux-aws-fips, linux-gcp-fips, linux-gkeop, linux-realtime, linux-azure, linux-azure-6.8, linux-azure-fde-6.8, linux-azure-fde, linux-oracle-6.8, linux-raspi, linux-raspi-realtime, linux-raspi, openjdk-17, openjdk-21, openjdk-25, openjdk-27, openjdk-8, openjdk-lts, perl, and pyasn1).

- Miniature industrial IoT gateway with dual Gigabit Ethernet and optional Wi-Fi 6, LTE
Compulab has detailed its IOT-GATE-IMX8PV2, a fanless industrial IoT gateway powered by NXP�s i.MX8M Plus processor. The small-form-factor system combines dual Gigabit Ethernet, optional Wi-Fi 6 and LTE connectivity, and isolated industrial I/O in a 105 � 80 � 30mm aluminum enclosure. The gateway uses a quad-core Arm Cortex-A53 processor running at up to 1.8GHz,0
- Google Summer of Code mentor summit 2026
Every year, the Google Summer of Code (GSoC) Mentor Summit brings together open source maintainers, community leads, and mentors from across the globe. It is an energizing unconference where the diversity of open source can be touched. This is a unique occasion to share what works (and what doesn�t) across0
- Running Android apps on Ubuntu is surprisingly easy
Ubuntu doesn�t run Android apps and games natively, but Waydroid is an open-source effort that lets you use them � and it�s now really easy to setup on Ubuntu. Earlier this year, Waydroid was packaged in Debian. That put it a simple apt install away on Ubuntu 26.04 LTS and later. No need to add a PPA, find a third-party package or run scripts from Reddit threads. Waydroid runs a containerised0
- AMD EPYC 9686F Linux Benchmarks: 96 Zen 6 Cores At Up To 5.3GHz
In addition to the AMD EPYC 9996 256-core CPU benchmarks out today in that dual socket configuration for a combined 512 cores / 1024 threads flagship Zen 6C server configuration, also tested recently at Phoronix was the EPYC 9686F part. The AMD EPYC 9686F is their new high-frequency Zen 6 part that features 96 cores / 192 threads at a boost clock of 5.3GHz! When the AMD EPYC 9686F they originally0
- Sprout upgrades your old iPod using Raspberry Pi & Linux
A new hardware project is using open-source hardware and software to breathe new life � and modern capabilities � into decades old iPods. Sprout, by London-based FOSS folk Certain Things, is a modern motherboard for old iPods! that requires no soldering. It re-uses all of the iPod�s original parts, including the screen, click wheel, case, etc. The idea is you split open your old device, remove0
- Euclid Mission Data Release Spans More Than 900 Million Galaxies
The European Space Agency has released the largest dataset yet from its Euclid space telescope, containing 1.7 petabytes of observations covering more than 900 million galaxies. "The data unveiled on Thursday covered a survey of the sky equal to about 9,500 times the size of the moon as viewed from Earth," reports Reuters. "The mission's goal is to complete the "largest-ever three-dimensional atlas of the cosmos, spanning more than a third of the sky, in 2031." From the report: "It marks a major milestone for ESA's Euclid mission and for everyone involved," said astrophysicist Valeria Pettorino, ESA's Euclid project scientist. Euclid, launched from Florida in 2023, is gathering data on how the universe has expanded and how its structure has formed over time while amassing information about the nature of dark energy and dark matter and the role of gravity on large scales. "Euclid will not just take images of galaxies in the sky, in two dimensions, but will also measure their distance, the third dimension. This will tell us where galaxies are in space and time, across 10 billion years, and in all directions beyond our galactic plane," Pettorino said. "Galaxies cluster along filaments, surrounded by empty space, and form a network that we call the cosmic web. Euclid will reconstruct the cosmic web and how it has grown over time. This is important because the exact configuration of the cosmic web, how many clusters or voids are there, how fast it changed, depend on the properties of dark energy and dark matter," Pettorino said. [...] Previous Euclid data releases covered only a few days of observations. The newly released dataset includes more than a year of data and still spans only 14% of the total sky area Euclid is due to survey in visible and near-infrared light over six years. This data release will be completed next year with the first results on dark energy and dark matter.
 
Read more of this story at Slashdot.
- SpaceX To Invest $74 Billion Into Data Center Construction Projects In Texas, Arizona
An anonymous reader quotes a report from the Hill: Elon Musk's SpaceX plans to invest more than $74 billion into building two data centers in Texas and Arizona, the company announced Thursday, marketing them as projects that will boost local communities amid backlash surrounding such facilities. "These investments will expand local tax bases, generate substantial new revenue for schools and public services, and create economic opportunities that extend far beyond the facilities themselves," the company said in a release. SpaceX said it will put more than $24 billion into a new project in Texas's Rio Grande Valley, expanding the company's headquarters in Starbase -- a coastal town the tech giant established in 2025 in a previously unincorporated area of Cameron County. In Arizona, SpaceX will invest around $50 billion in Cochise County, a rural area east of Tucson bordering Mexico and New Mexico. SpaceX pledged the new projects will be created cooperatively with the surrounding communities and will be environmentally conscious. The company said the project in Texas would generate its own power and invest $220 million to expand the water supply in nearby Brownsville. While in Arizona, it vowed to work with local electric cooperatives and "potentially" reduce electric bills, saying the site would use dry cooling without water consumption. "They require strong partnerships with local communities, responsible environmental stewardship, and stable, competitive policies that give companies the confidence to make long-term investments," the company said in a release. Both sites promise hundreds of permanent jobs even once construction is complete.
Read more of this story at Slashdot.
- Whoop Launches a Social Network Where Every User Has a 'Verified Heartbeat'
Whoop has launched Humans, a social network built into its fitness app where every account is a real person with a "verified heartbeat." The wearable company claims its platform is "entirely human," unlike other social media platforms that are "saturated with artificial intelligence, automated accounts and bots, and manufactured content." The Verge reports: Starting Thursday, Whoop members can share their data from its wearables on the app's new Whoop Humans social network. Users can make their metrics, activities, and achievements visible to other Whoop wearers, post Story-like "Moments" with photos and captions, and add comments and reactions on other members' posts. [...] In the Community tab in Whoop's app, users can scroll through Moments from people they're following, like tapping through your Stories feed on Instagram but with your friends' fitness tracker data. In one of Whoop's examples, swiping up on a user's Moments post with a photo from their run shows a map with their route and details like their pace and distance. The Community tab also shows cards for people in your "community" with their sleep, recovery, and strain scores. Whoop says users choose which activities, achievements, and metrics they want to share on Humans, including Recovery, Strain, Sleep, HRV, and resting heart rate. Any activities marked as sensitive aren't shared by default. There's also an option to keep Moments posts private and a "Stealth Mode" for temporarily hiding health and performance data without changing your sharing settings.
Read more of this story at Slashdot.
- Nintendo Takes Down Switch Emulators, Mod Chip Firmware in Massive GitHub DMCA Sweep
Nintendo has issued four DMCA takedown notices targeting two Nintendo Switch emulators, Yuzu and Citron Neo, along with mod chip firmware such as Picofly, SX Core and HWFLY. As a result, 144 repositories containing firmware used to circumvent the console's copy protections have been removed by GitHub and replaced by a DMCA takedown notice. IGN reports: GitHub has posted Nintendo's November 6 DMCA notice, which says, "The Nintendo Switch console and video games contain technological protection measures ('TPMs') that permit the Nintendo Switch console to interact only with legitimate Nintendo video game files. This process protects Nintendo's copyright-protected video games, (...) by preventing users from playing pirated copies of Nintendo's video games on the Nintendo Switch console and by preventing users from unlawfully copying and playing Nintendo's video games on unauthorized devices." However, while this takedown has effectively wiped out a ton of repositories with mod chip firmware, it seems like it's still being hosted elsewhere on the site, according to TorrentFreak. It's possible, though, that Nintendo isn't finished yet; back in 2024, Nintendo effectively took down 8,500 copies of Yuzu by issuing a takedown that targeted 12 different mirrors of the emulator. This particular takedown also comes a few days after emulators were able to run the remake of The Legend of Zelda: Ocarina of Time on PC, so this could be a sign that Nintendo is winding up its lawyers to crack down on emulation once again.
Read more of this story at Slashdot.
- Former Nvidia CEO Jensen Huang Had a Relationship With a Second Employee
Reuters reports that former Nvidia CEO Jensen Huang had an intimate relationship with a third woman (source paywalled; alternative source ), an unnamed Nvidia employee. The revelation follows reports of two other extramarital affairs: one with Nvidia VP Kimberly Powell and another with Alice Huang, whom U.S. intelligence reportedly suspects of being a Chinese spy. The latter relationship has also prompted a shareholder lawsuit alleging Nvidia misled investors about its ties to a company suspected of circumventing U.S. chip export restrictions. Jensen Huang has since resigned as Nvidia's CEO and stepped down from its board on Thursday. CFO Colette Kress has been appointed interim CEO while the company searches for a permanent successor.
Read more of this story at Slashdot.
- Singapore Says US Not Helpful On Investigation Into Suspected Spy's Company
Singapore says U.S. authorities provided limited assistance in its investigation of Megaspeed, the company run by Alice Huang, the Chinese businesswoman whom U.S. intelligence suspects is a Chinese spy and whose relationship with Nvidia CEO Jensen Huang has drawn scrutiny. According to Singapore, authorities held Alice Huang's passport from June 2025 until February while investigating "potential false declarations," but ultimately released her with a "stern warning" and barred her from re-entering the country. The New York Times reports: The statement raises new questions about the response of the Trump administration to the case and why the U.S. government did not more forcefully intervene. According to the timeline in the statement, Singaporean authorities had been holding Ms. Huang's passport well after President Trump was briefed last fall about her relationship with Nvidia's chief executive and the belief that she was a Chinese intelligence asset. The New York Times has reported that Taiwan began monitoring Ms. Huang in 2024 at the guidance of the U.S. government. In its statement, Singapore said that it had sought information from an American server maker and close Nvidia business partner, Supermicro, but that the company had provided "limited cooperation." Supermicro, a firm that packages Nvidia's A.I. chips onto servers that can be used in data centers, has been at the center of a number of chip smuggling investigations across the globe. Supermicro was a supplier to Megaspeed, a company incorporated in Singapore and run by Ms. Huang, according to two people with knowledge of the matter. Singapore said in the statement its authorities raised Supermicro's "limited cooperation" with the U.S. Department of Justice and Federal Bureau of Investigation in July 2025 and "requested their assistance in securing the company's cooperation." "Despite these repeated requests, Singapore has to date received limited information or assistance in respect of the company," the statement said.
Read more of this story at Slashdot.
- Microsoft Outlook Goes Down Nationwide [UPDATE]
Microsoft is suffering a major Microsoft 365 outage that's disrupting Outlook, Teams, Copilot and SharePoint for users across the Americas, with more than 129,000 problem reports logged on Downdetector shortly after the disruption began. Microsoft blames the connectivity problems on an unexpectedly large number of unavailable servers that overloaded the remaining infrastructure. The company says it's redistributing traffic and restarting affected systems. From a report: Microsoft was not providing an estimated time by which it expects service to return. Both individual Outlook users and those on enterprise accounts experienced problems logging in to the service. The outage also affected other Microsoft services, including Microsoft Teams, the Copilot 365 AI service and SharePoint Online. "Users may be unable to connect to multiple Microsoft 365 services," the company said on its Service Health Status page. UPDATE 11/12/26, 19:50 UTC: From Microsoft 365 Status: "We're testing a configuration change to address a problem that's causing servers to fail automated health checks and become unavailable. In parallel, we've initiated a restart of all affected servers and are monitoring health as they return to service. More info under EX1550543 and MO1550821 in the Microsoft 365 admin center, as well as http://status.cloud.microsoft if the admin center is not available to you." UPDATE 11/12/26, 20:19 UTC: From Microsoft 365 Status: "We've not identified any recent change correlated with the start of impact; however, our investigation indicates the failed health checks may originate from a specific component that's responsible for processing server health. We've taken steps to prevent additional servers from being impacted while we work to return the affected servers to service. More info under EX1550543 and MO1550821 in the Microsoft 365 admin center, as well as http://status.cloud.microsoft if the admin center is not available to you. UPDATE 11/12/26, 20:29 UTC: "According to https://downdetector.com/, much of the major services are down," writes Slashdot reader xocmot2. "AWS, Microsoft, Meta, on and on. Clearly not a Microsoft thing." UPDATE 11/12/26, 6:17 UTC: Microsoft is still struggling to resolve the outage, which is confirmed to be global with disruptions reported across 74 countries and territories. The outage has disrupted businesses and government services in countries including Japan, Singapore, India, and Australia, while OpenAI and Anthropic have also reported related problems. Microsoft says its recovery efforts have produced some improvements, but the fixes are not delivering "sustained recovery." Microsoft has ruled out a cybersecurity incident, and experts warn that the prolonged disruption could result in significant economic losses. Developing...
Read more of this story at Slashdot.
- Google Pushes Privacy Angle As Gemini-Powered Smartglasses Debut
Google is launching its first Gemini-powered smart glasses, with Samsung supplying the computing hardware. Given their built-in 12-megapixel camera, Google is emphasizing privacy protections, including a tamper-resistant recording light, automatic face redaction, and restrictions on real-time facial recognition and livestreaming. The company also promises not to use captured photos or videos for AI training or targeted advertising. Ars Technica reports: Google says the frames all weigh about 41 grams, which is not terrible but is definitely near the top for glasses generally. They will, naturally, weigh much more when you account for lenses. That will also determine the final pricing. So far, we only have the starting prices for these devices, including non-prescription lenses. The setup here is similar to the Ray-Ban Meta glasses we've seen for a few years. There are no screens in the lenses, but you can interact with the AI system via voice or by activating the integrated camera. The experience should be similar to using Gemini Live on your phone, but it will be a lot easier to fire up the AI. You can say "Hey Gemini" or tap a touch-sensitive area of the frame to start interacting with the robot. Since this is the same chatbot that operates across the Google ecosystem, it has access to your data and preferences. You can ask questions and get personalized answers, have Google Maps guide you by voice, or just talk with the AI to kill time. The glasses use custom open-ear speakers to limit distractions for those around you. Google notes the directional microphones should not pick up speech from other people, either. Adding the camera feed is where things get interesting. When the AI can see what you see, it has the potential to do more work on your behalf. Google suggests asking Gemini for recommendations when looking at a bookshelf or glancing at an event poster to have the AI add it to your calendar. The glasses will also support Gemini Guided Vision, which provides conversational audio descriptions for people who are visually impaired. The new frames are available for preorder today starting at $395.
Read more of this story at Slashdot.
- Iconic First Image of Black Hole Holds Up To Scrutiny
An anonymous reader quotes a report from The Conversation: On April 10 2019, the Event Horizon Telescope (EHT) Collaboration revealed the first picture of a black hole. The object is at the centre of a galaxy known as M87, about 55 million light-years away. The iconic ring structure instantly became one of the most recognized scientific images of the modern era. It showed a black hole "shadow" outlined by light from swirling hot gas -- just as predicted by Einstein's theory of general relativity. The result supported the long-standing idea that the centers of galaxies house supermassive black holes. However, scientists have since had some disagreements on whether the details and structure of the ring in the original publication were accurate. Our new research, published today in Nature, used new techniques to investigate the original datasets. Not only do our results validate the original work, but they also provide a fresh perspective on the ring structure. Our independent results enhance confidence in one of the most significant modern scientific results. And we bring the image of a black hole millions of light-years away back into focus. [...] When compared directly to images from the EHT collaboration, our result is consistent in diameter and overall orientation. Naturally, there are some differences in the fine details of ring width and surface brightness along the circumference, but the overall structure matches. This provides a fresh perspective on the iconic black hole ring while also resolving previous discrepancies. To prove this success didn't depend solely on advanced machine learning, we also developed a complementary imaging method based on traditional statistical techniques. This entirely different method also validated our structure using the new closure invariant data we produced. Overall, our work delivers a strong independent validation of the supermassive black hole structure at the centre of galaxy M87. And it could do more in the future. Our technique could also be useful in other situations where data from multiple sensors are combined to map unknown structures -- such as medical imaging or mapping earthquakes.
Read more of this story at Slashdot.
- Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely
A critical flaw in Apache HTTP Server's HTTP/2 module could allow unauthenticated attackers to remotely execute code and potentially take control of affected server processes. Tracked as CVE-2026-119618, the vulnerability affects Apache HTTP Server 2.4.55 through 2.4.70 when HTTP/2 is enabled and is fixed in version 2.4.71. The Hacker News reports: The vendor's assessment, published yesterday, also says "public research has demonstrated a reliable exploit" against a server in its default configuration with mod_http2 enabled. It does not name or link that research. Security company Wiz said later that day that no exploit was available and that no exploitation in the wild had been reported. HTTP/2 runs only where the Protocols directive turns it on, as the module documentation explains. The directive uses h2 for HTTP/2 over TLS and h2c for HTTP/2 over plain TCP. It can be set for the whole server or for a single virtual host, so admins should check the server-wide setting and every virtual host. Standalone builds of the module, released on GitHub as mod_h2, are affected from version 2.0.8 through 2.0.42. Admins who run the Apache HTTP Server project's own releases should move to version 2.4.71, the fixed release named in its security advisory. That release also fixes a crash in mod_md, rated important, and a one-byte overwrite of stack memory in mod_vhost_alias, rated low.
Read more of this story at Slashdot.
- Jensen Huang Resigns As Nvidia CEO
Jensen Huang has stepped down as CEO of Nvidia after 33 years leading the company, with CFO Colette Kress taking over as interim CEO while the board searches for a permanent replacement. "The Board has full confidence in Colette and the leadership team, and we expect the company's operations, customer commitments and product roadmap to continue without interruption," said board chair Harvey Jones in a release announcing the news. The abrupt departure follows revelations about Huang's affairs, including one with a woman U.S. intelligence reportedly believes was a Chinese spy. CNBC reports: Huang, 63, apologized on Sunday for being "unfaithful to my wife," though he provided no details about the affair with businesswoman Alice Huang, who has worked for a Chinese company and Nvidia customer called Megaspeed. Late Wednesday, The New York Times reported that the Nvidia CEO also had a separate affair, this one with Kimberly Powell, vice president of health care at the chipmaker. Later that afternoon The Times and other outlets reported that Nvidia's board met to discuss the company's future. Jensen Huang denied allegations that he had compromised national security or Nvidia secrets after reports of the Alice Huang affair. The news sparked concerns that Nvidia knew companies based in Singapore and Malaysia had been evading U.S. export controls in accessing its technology. The board said on Tuesday that it had hired Wachtell Lipton to investigate the intelligence allegations.
Read more of this story at Slashdot.
- Tim Peters, Python User #2 and Prolific Contributor, Dies At 74
Tim Peters, one of Python's earliest and most influential contributors, died on July 15 at age 74. Known as Python's second real user, Peters created the Zen of Python and Timsort sorting algorithm while contributing to numerous core components. He also served as a Python Software Foundation director from 2001 to 2014. Adafruit remembers Peters in a blog post: He's best known for the Zen of Python, PEP 20, still printed by typing import this. In 2002, he gave Python Timsort, the sorting algorithm he designed for lists, later adopted by Java and Android. He also polished the cyclic garbage collector and the pymalloc allocator, worked on the dict implementation, the float object, the math module and Karatsuba multiplication in longobject, and wrote the first version of doctest, plus difflib, pickletools and tabnanny. He was a director of the Python Software Foundation from 2001 to 2014. Before Python, he wrote compilers at Cray Research and speech-to-text software at Dragon Systems. The thread is full of recollections from core developers about his patient, detailed answers on the mailing lists, signed with his trademark . Python creator Guido van Rossum also paid tribute to Peters in a post on discuss.python.org, writing: "It's hard to overestimate Tim's influence on Python. He's probably best known for writing the Zen of Python (PEP 20), but to me he was a mentor and language co-designer long before that..." Further discussions can be found on Hacker News and Reddit.
Read more of this story at Slashdot.
- Power Grids On 5 Continents Pulse Every 60s. Scientists Think They Know Why
"ScienceAlert is reporting that researchers may have finally determined why, for many years, power grids around the world have been pulsing every 60 seconds," writes longtime Slashdot reader fahrbot-bot. The likely culprit? Uninterruptible power supplies running routine battery checks. From the report: Every minute, some uninterruptible power supplies perform routine battery checks, creating small but measurable surges in electricity demand. And it's like clockwork. "Even benign control routines can become systemically relevant when many devices act coherently," writes a team led by physicist Dirk Witthaut of the University of Cologne, Germany, in a paper published in Nature Energy. "Unintended synchronization can generate recurrent and potentially amplified oscillatory behavior in large-scale cyber-physical energy systems." To figure it out, Witthaut and his colleagues analyzed high-resolution electricity measurements from buildings at the Forschungszentrum Julich research campus in Germany. [... they found that] the 60-second pattern appeared in four buildings, all of which contained uninterruptible power supplies. None of the buildings they measured without these systems showed the same pattern. Following the electrical signals more closely, the researchers detected tiny bursts of current from the batteries at precisely one-minute intervals. They were able to trace the resulting fluctuations through one building's electrical system, all the way to the connection with the public high-voltage grid. The manufacturer subsequently confirmed the culprit's identity -- routine battery self-tests, conducted automatically by the systems' management software. But why would equipment in different buildings, let alone different countries, be doing this at the same time? The answer appears to lie in the clocks. Digital devices can synchronize their internal clocks using external time signals, meaning that independently operating systems can end up performing their scheduled tasks together. Individually, these small checks are insignificant. But when enough devices act in synchrony, their combined electricity demand can produce a measurable effect across an entire power grid.
Read more of this story at Slashdot.
- Sunken SS United States Set To Become World's Largest Artificial Reef
An anonymous reader quotes a report from PBS: The historic ocean liner SS United States will be intentionally sunk Wednesday off the coast of the Florida panhandle. Live coverage of the sinking of the SS United States is expected to start at 1 p.m. EST, with the sinking expected at 2 p.m. EST. Watch live in the video player above. In its heyday, the SS United States crushed the trans-Atlantic speed record, which it still holds. The luxury ocean liner took only three days to cross from New York to Europe on its maiden voyage in 1952. Carrying presidents and Hollywood stars, the nearly 1,000-foot vessel was a technical marvel of its time. However, the rise of air travel and high operating costs sunk its economic viability, and the ship was pulled from service in 1969. The ocean liner sat at Philadelphia's Pier 82 for nearly 30 years. After a contentious back and forth with a pier landlord over rent and docking fees, Okaloosa County in Florida eventually stepped in to purchase the ship and bring it to the Gulf of Mexico to become the world's largest artificial reef. The multi-million dollar project is also aimed at creating an economic development opportunity as a major diving attraction. "It was our goal to make sure that she wasn't lost forever," said David Lawrence, a member of the board for the SS United States Conservancy, the group that sold the vessel to the Florida county. Like the ship's unconventional life, it will also have an unconventional sinking. Federal environmental and explosives rules prevent the county from using explosives. Instead, tanks inside the ship have been removed and large holes were cut into the decks. Once the valves are opened, water will flood the hull, sinking the ship. Resting at 180 feet below the surface of the water, the SS United States will join more than 500 artificial reefs in Okaloosa County, which the county relies on to support the underwater ecosystem.
Read more of this story at Slashdot.
- United Airlines Bans AI Agents From Booking Flights On Behalf of Travelers
United Airlines is banning unauthorized third-party AI agents from booking flights, checking in passengers or making account changes on travelers' behalf. CBS News reports: To make an airline booking, an AI agent requires access to a customer's personal information, including credentials like payment information. United has a problem with that, saying that "sharing account credentials with personal, third-party, AI assistants can expose sensitive information, and actions taken by these tools may result in unintended purchases, account changes, or use of MileagePlus miles." The carrier also said that using an AI agent to, for example, check in for a flight could violate federal regulations, including rules requiring travelers to verify in person that their luggage does not contain banned substances. "As a result, United is taking steps to restrict access -- directly within our digital platforms and indirectly via travel agencies and aggregators -- to prohibit use by unauthorized, third-party personal AI agents or assistants," said the airline, which is updating its booking and ticketing policies to reflect the new rule. "United is saying they don't want to add yet another, and potentially even more powerful, intermediary than they already face in terms of Google search, price-comparison metasearch sites and online travel agencies," said Henry Harteveldt, an aviation analyst at Atmosphere Research Group. "Flight searches cost airlines money, and undoubtedly United wants to avoid the expense associated with the surge of AI bot flight searches."
Read more of this story at Slashdot.
- From DHCP to SZTP – The Trust Revolution
By Juha Holkkola, FusionLayer Group The Dawn of Effortless Connectivity In the transformative years of the late 1990s, a quiet revolution took place, fundamentally altering how we connect to networks. The introduction of DHCP answered a crucial question, Where are you on the network?!, by automating IP address assignment. This innovation eradicated the manual configuration [0]
The post From DHCP to SZTP – The Trust Revolution appeared first on Linux.com.
- OpenAI Codex Helps Uncover & Fix A Nearly 20 Year Old Radeon Linux Driver Bug
Sent out today was the latest batch of AMD kernel graphics/compute driver patches destined for the Linux 7.5 merge window opening up at year's end/ Besides a lot of fixes and continued work around new IP enablement for upcoming GPUs, there is even a fix for old ATI/AMD Radeon R600 era hardware after help from OpenAI's Codex...
- AMD Zen 6 SMT Proves Very Advantageous Even For 256 Core EPYC 9996
With the now-shipping AMD EPYC 9006 "Venice" SP7 server processors sporting up to 256 Zen 6(C) cores per socket, or 512 cores in a 2P configuration, you may be wondering if Simultaneous Multithreading (SMT) is still worthwhile on these increasingly high core count processors. Long story short, SMT on AMD Zen 6 is still definitely worthwhile from a performance and power perspective. I was curious myself and ran some benchmarks to explore the SMT impact on the 256-core EPYC 9996 as well as the 96-core high frequency EPYC 9686F processors.
- NVIDIA CEO Jensen Huang Resigns
Following reports of two extramarital affairs, one with an alleged Chinese spy and the other with a VP that is a direct report to him, Jensen Huang is no longer CEO of NVIDIA...
- AMD EPYC 9006 Venice vs. NVIDIA Vera Benchmarks For HPC Performance
Yesterday in the AMD EPYC 9006 "Venice" SP7 launch testing were reviews of the AMD EPYC 9996 256-core processor as well as the EPYC 9686F 96-core high frequency part. There were hundreds of benchmarks looking at the gen-on-gen performance from EPYC Turin to EPYC Venice as well as against the Intel Xeon 6 Granite Rapids competition. For those wondering about how AMD EPYC Venice is competing with NVIDIA9s Vera CPU, this article provides a look at those results for a range of HPC workloads.
- ATI/AMD R300 To R500 GPUs See New 2026 OpenGL Linux Driver Optimizations
Over 24 years old, the ATI (AMD) Radeon R300 graphics processors are still seeing improvements in the open-source Linux driver space. Merged to Mesa 27.0-devel this week were a number of shader compiler optimizations for the R300g driver that benefits not only the original R300 series graphics cards but also the R400 and R500 (Radeon X1000 series) too...
- Intel Releases New CPU Microcode To Fix A Variety Of Functional Issues
Intel on Tuesday released the microcode-20261110 package that ships updated CPU microcode binaries for recent Intel Core (Ultra) and Xeon processors. The updated CPU microcode is for Core Gen 13 "Raptor Lake" and newer while on the Xeon server side is for Sapphire Rapids and newer. This is also the first time Clearwater Forest has seen microcode updates...
- AMD EPYC 9996 Benchmarks Show Unparalleled Performance With 256 Zen 6C Cores
Back in July AMD announced the EPYC 9006 "Venice" series at their Advancing AI event. Today they are announcing EPYC 9006 series Socket SP7 processor availability and with systems beginning to ship today from their OEM/ODM partners. With that we are also now allowed to begin sharing AMD EPYC 9006 performance benchmark figures. Back in July I expected EPYC 9006 to be a "grand slam" for performance... After hands-on with the 6th Gen EPYC processors, it9s a grand slam alright -- out of this world.
- AMD EPYC 9686F Linux Benchmarks: 96 Zen 6 Cores At Up To 5.3GHz
In addition to the AMD EPYC 9996 256-core CPU benchmarks out today in that dual socket configuration for a combined 512 cores / 1024 threads flagship Zen 6C server configuration, also tested recently at Phoronix was the EPYC 9686F part. The AMD EPYC 9686F is their new high-frequency Zen 6 part that features 96 cores / 192 threads at a boost clock of 5.3GHz! When the AMD EPYC 9686F they originally disclosed a 5.0GHz boost clock but with how well their production silicon panned out and/or marketing reasons, it9s actually now confirmed to be 5.3GHz in production.
- AMD Talks Up Their MEXT Software Amid RAM Crisis - Linux Support But Not Open-Source
This summer AMD acquired the company MEXT for their AI-powered predictive memory technology to make flash memory such as NVMe SSDs behave more like DRAM. AMD MEXT with EPYC servers allows for flash memory as DRAM tiering and uses a predictive AI engine for handling the tiering in an effective way. There is a Linux driver but this is one of the few offerings in the AMD space that isn't open-source as part of their typical open ecosystem approach...
- AMD EPYC Embedded 9006 Series SP7 Announced
In addition to today's announcement of AMD EPYC 9006 SP7 availability, complete with reviews of the AMD EPYC 9996 256-core flagship and EPYC 9686F 96-core 5.3GHz part, AMD also announced the EPYC Embedded 9006 Series SP7 processors...
- openSUSE Tumbleweed Transitioning To Agama Installer
With openSUSE Leap making use of the modern Agama installer developed by SUSE engineers, the rolling-release openSUSE Tumbleweed is now preparing to make the same transitioning in replacing the YaST Installer...
- ReactOS makes strides in SMP, 64bit, and more
The ReactOS project organised two hackfests this year, and the work done during those in-person sessions, combined with the ongoing regular progress, has led to some pretty significant breakthroughs and progress. More NT6+ syscalls have been added, ReactOS supports floppy disks now, NTFS support has been vastly improved, and much more. There�s also a new USB3/4 stack, which is now merged and offers basic support for these versions of USB. One of the biggest additions is a new kernel shim engine which gives ReactOS the ability to work around buggy drivers and implement quirks, moreso than even Windows itself can. For instance, thanks to this new shim, XP-era NVIDIA drivers can run on NT6 ReactOS. The ongoing efforts to implement SMP are yielding results too: ReactOS can now run with SMP for days on end while doing tasks in the background, which is quite promising. The team is showing off Steam and the game Among Us running on ReactOS, which is definitely impressive.
- Polo: a new Wayland compositor for MATE
MATE is probably the last X11-only holdout among the major desktop environments, but that�s about to change if Kerem Söke has anything to say about it. Polo is a port of Marco�s behavior and window management policies to Wayland, built on libweston and written in Vala and C. It�s a window manager, compositor, and session authority for the MATE Wayland desktop. It takes over, step by step, what Marco, mate-session-manager and the compositor-facing parts of mate-settings-daemon do on X11. ↫ Polo�s GitHub page Söke is looking for testers with this very first Polo 1.0.0 release � cute name, too � which is available on its GitHub page.
- IBM to offer access to a dual-processor quantum system in 2027
Ars Technica published a short write-up about changes to IBM�s quantum computing plans. The changes greatly expand the scope of its next-generation Nighthawk general-use processors by adding a version with over 500 programmable qubits. At the same time, it’s stepping back a bit on its plan to link multiple Nighthawk processors together, dropping the intended number of linked systems from nine to two. The total number of qubits planned for next year will remain the same; how the company is getting there, however, will be different. Meanwhile, the company is touting the performance boost achieved via a major change that was made in the generation of Nighthawk processors released in September: hardware-based qubit resets. ↫ John Timmer at Ars Technica I�m convinced quantum computing will eventually have a big impact in the areas its characteristics are presumed to be well-suited for. Also, it just looks and sounds incredibly cool, even if as the technology currently stands it�s not particularly useful yet.
- I�m not descending into madness because mount and unmount icons make no sense
There are many problems in this world � some big, some small, some so minute nobody ought to put them to paper at all. The problem I�m going to highlight here is even smaller than that. This literally � the actual literally � does not matter and absolutely nobody should care about it, let alone put any work into changing it or addressing it some other way. I want to talk about the iconography GNOME�s Disks utility uses to symbolise mount! and unmount!. No, I�m not descending into madness. GNOME�s Disks utility uses the play! symbol on the mount button, and the stop! symbol on the unmount button. Inexplicably, considering the state of the world in general and the rapidly deteriorating quality of software specifically, this bothers me. Out in the real world, built on decades of consistent use, these symbols have gained clearly defined meanings, and mounting and unmounting disks definitely isn�t one of them. In fact, the meaning of these symbols isn�t mere convention; they�re defined in a variety of international standards for symbols for use in software and on equipment, such as ISO/IEC 18035 (which you need to buy to read; my copy fell of a truck): ISO/IEC 18035:2002 defines a consistent set of icons and related functions that are represented by multimedia applications on a computer screen and that users interact with to control such applications. It describes controls applying to such functions as: Play, Pause, Stop, Rewind, Scan forward, Scan backward, Replay backward, Loop, Go to beginning, Go to previous, Go to next, Go to end, Set volume and Mute. ↫ ISO/IEC 18035:2003 They�re also part of ISO 7000/IEC 60417, a much larger, more encompassing standard that also contains things like the various symbols used on laundry machines, tumble dryers, in cars, and so on. The symbols themselves are much older than the standards, of course, with many of them dating back to the 1960s and possibly even 1950s. The point remains, though: the play and stop symbols have clearly defined meanings, and I don�t think they are at all a good fit for mount and unmount. The function of the play! symbol according to ISO/IEC 18035: To enable the user to start the presentation of dynamic media, except where the task requires automatic playing of that media. ↫ ISO/IEC 18035:2003 And of the stop! symbol: To enable the user to stop the presentation of dynamic media. ↫ ISO/IEC 18035:2003 Neither of these descriptions match what mounting and unmounting mean or do. Mounting a drive or partition doesn�t present any media at all; it merely makes the drive or partition in question accessible. Unmounting also doesn�t eject anything; it merely makes the drive or partition inaccessible. I would argue that play and pause act upon contents of a drive or volume, and not upon the drive or volume itself. As it stands right now, you play! a drive! to play! a video stored on said drive. Madness. I already know what you�re thinking, and yes, I agree that the Disks utility is a tool aimed at more advanced use cases and users, and most normal, average users will never even know it exists, let alone open it at all. Very few people get to see these symbols, and those that do already know full well what mounting and unmounting mean, reducing the importance of said symbols considerably. But now it�s time for the big surprise, the twist in the story that turns this entire thing on its head. Files, GNOME�s file manager, uses an entirely different symbol for unmounting! Instead of the stop! symbol, Files uses the eject! symbol. You may think this is a more accurate visual representation of what unmounting means, but I strongly disagree. Let�s turn to ISO/IEC 18035:2003 once again: To enable the user to eject the current physical media from the appropriate drive. ↫ ISO/IEC 18035:2003 Unmounting doesn�t eject anything! If you unmount a USB stick, the stick doesn�t get fired out of the USB port. If you unmount a volume, it doesn�t get removed from the SSD. Hell, if you unmount a CD-ROM, it doesn�t even eject it! Ejecting a CD-ROM � opening the drive�s tray or spitting the CD-ROM out of a slot-loader � is an entirely different act! Are we really ejecting! a CD-ROM twice? Are we mounting! a CD-ROM when we merely close the tray? No! Madness! The real underlying problem here is, of course, that mounting and unmounting are deeply weird and confusing concepts, bordering on the esoteric, that simply do not have physical equivalents to fall back on. Using symbols and iconography designed in the 1960s explicitly for playing music or stopping a video or ejecting a cassette tape are not a good fit for something as difficult to explain to most people as mounting and unmounting. It�s like putting an eject symbol on a car�s door handle or a play symbol on a soap dispenser. Should GNOME developers waste any time or resources to address this? No, of course not, that would be stupid. Nobody should care about this but me. I should suffer in silence, every time I need to mount or unmount something, forced to look for an eject or stop symbol in whatever user interface I happen to be using. Every time, I should die a little inside. Please, don�t be like me and waste precious resources thinking about this. I�m not descending into madness. I just want mount and unmount symbols that make sense. I�m not descending into madness.
- Haiku gets multifinger touchpad taps
We�re almost halfway through November, but we hadn�t seen Haiku�s monthly activity report for October yet. It�s here now, and there�s quite a few good things in here, like support for two and three-finger tap gestures on touchpads for right and middle-click, a new driver that adds Universal Flash Storage support, and even some build fixes for Haiku�s SPARC port as well as some fixes on the RISC-V side. Of course, that�s just a selection, as there�s the usual long list of smaller changes, bugfixes, and improvements as well.
- Microsoft releases .NET 11
Today, we’re excited to announce the release of .NET 11! This year’s release makes building modern applications faster, more productive, and has improvements across C# 15, ASP.NET Core, .NET MAUI, and Windows development. With hundreds of runtime optimizations, more responsive SDK tooling, and less overhead in everyday commands, you can spend less time waiting and more time creating. Build richer web and cross-platform applications, take advantage of new C# language features, and explore AI-powered development with improved tools and agentic capabilities. ↫ .NET Team I�m not going to pretend to care about .NET, but I know many of you have to care on a professional level, because .NET is remarkably popular in places where the spotlights don�t often shine.
- What if any process could handle SIGKILL?
An interesting question, and a detailed technical rundown of how to make this happen, which involved building a custom Linux kernel, of course. I really, really enjoy the conclusion. And you know? It turned out fine. Nothing exploded on my system. As I could predict, because this was otherwise impossible, nobody did it. The signal system was setup in such a way that you would most likely realize something you were doing was wrong, and not try it. To pull back further, it is interesting to notice how the rules we all take for granted are just set somewhere in code. They were written by someone, at some point. If there is code restricting you from doing something, someone wrote it. Either they did not think anyone would want to do that thing, or they specifically prevented you from doing it. Those rules are written somewhere, and you can take it in your paws to go sniff around the code, pull out the relevant parts, and hack around the things that bother you. For fun, learning, or convenience. Snoop around. Sniff code. Put your paws in it. Hack shit. ↫ lux at VulpineCitrus Even if there�s no real reason to do, even if it�s just to satiate an odd and possibly slightly morbid sense of curiosity, fuck with code.
- OpenIndiana Hipster 2026.10 released
OpenIndiana is a rolling-release illumos distribution, but they do release snapshots twice a year to serve as a base for installations, which they call Hipster. The project�s just released OpenIndiana Hipster 2026.10, and it brings a number of welcome changes. First, there�s UEFI framebuffer support on the live image, which is automatically configured when loading up the image. Second, Firefox and Thunderbird versions have been bumped to 159.0, and a whole slew of development tools have been updated to newer versions as well. This snapshot also brings QEMU 11.1.2 and VirtualBox 7.2.22, and a number of new applications have been added as well. In addition, SPARC build support has been improved to enable new and updated packages for Sun�s dead ISA as well. You can download a fresh image, or update an existing installation through IPS.
- Making musl and proprietary NVIDIA drivers work together
Creator and lead developer of Chimera Linux, Nina q66!, write about their efforts to get NVIDIA drivers to work properly on musl-based distributions. As you may be aware, one of the limitations of musl-based distributions is that they will not function to their proper extent when used in computers with various NVIDIA graphics cards. This is due to the proprietary nature of the driver, being built for glibc. I have been experimenting with trying to make this work, and this post is the summary of that effort. ↫ Nina q66! on the Chimera blog What follows is a deeply technical exploration of the problem, and the steps Nina q66 and the Chimera team are taking to try and fix it. With how popular and widespread NVIDIA hardware still is, this is a hugely important issue to try and address, and I�m grateful they�re trying to address it.
- MorphOS 3.21 released with new office suite
About five months after the previous release, the MorphOS team has released MorphOS 3.21. It brings the usual list of big fixes and smaller improvements, but there�s a few big ticket items in here as well. MorphOS 3.21 introduces BasicWorks, an office suite made up of CellBasics and PageBasics. It offers document and spreadsheet authoring and loads and saves Microsoft Office and OpenOffice documents. Also new are NVMEMount, an auto-mounter for booting from and mounting NVMe partitions, and the Marbles and Cyber 3D blankers. Graphics performance has been improved, with a faster Radeon driver on cards with little video memory thanks to GART backed bitmap transfers, quicker TinyGL texture copies, hardware accelerated antialiased text in TTEngine and much faster color SVG glyph rendering in Cairo. The Bcm43xx wireless driver has been substantially reworked, with automatic transmit rate selection, updated firmware and numerous connection fixes. PowerBook and iMac hotkeys are now fully configurable. ↫ MorphOS 3.21 release announcement The BasicWorks office suite has been in the works for a while now, and more information on it can be found in a thread on the MorphZone forums and on the website for the spreadsheet component of the suite, CellBasics. The formula loaders and xlsx loaders are ports of open source projects, but the rest of the application is new code based on ObjectiveC++ and Cairo/Harfbuzz. It uses its own file format, but can import csv and xslsx files, so I�m assuming the same more or else applies to the word processor (but with docx, of course). Alongside MorphOS 3.21 also comes a new release for Wayfarer, the web browser the Amiga-inspired operating system uses. Wayfarer 12.0 moves to WebKitGTK 2.52.5 (which was released in July of 2026, so it�s quite up to date), and now uses the Skia graphics library. R300-R500 Radeons will render websites with Skia-GL for some massive performance improvements, helped further along by a slew of additional performance optimisations. Adblocking has been improved as well, YouTube should work a lot better now, and much more. The full release notes for MorphOS 3.21 give you all the details.
- The port that does not exist
Ask any program to listen on port 0 and it will hand you a socket on port 471930or 580370or whatever the kernel felt like that day. Port 0 is not a port you can have. It is the number you pass when you want the operating system to pick one for you. But a TCP header is just bytes. The destination port field is 16 bits wide, and 0x0000 fits in 16 bits as well as anything else does. Nothing on the wire stops a packet from being addressed to port 0. Your tools will refuse it, your browser will block it, and your scanner�s default port list skips it, because everyone agrees it isn�t a real port. Which makes it a pretty good place to hide things, whether anyone meant to or not. So we did some TCP cowboy shit 8 port scanned the entire fucking internet for open ports on port 0, which uncovered some interesting unexpected findings. ↫ acidvegas An awesome and entertaining read. Don�t skip this one.
- Windows 11 27H2 might be a more substantial upgrade
A little tidbit of news regarding the nest major update to Windows, known as Windows 11 27H2. Apparently, it�s going to come with some more serious changes to the codebase, therefore necessitating a full operating system swap instead of a mere enablement package, much like Windows 11 24H2 was. For those who need a refresher, Microsoft has long been rumored to be running on a three-year release cadence and for a while, it was even thought that the company would launch Windows 12 in 2H 2024. That evidently didn�t happen, as instead we got Windows 11 24H2, but it was a major upgrade, a full OS swap compared to Windows 11 23H2 and 22H2. Essentially, it looks like every three releases, Microsoft is performing a full swap with major changes in the underlying codebase, and it seems to line up with Windows 11 27H2 as well. At the moment it�s not known if system requirements will change or not. ↫ Sayan Sen at Neowin.net Microsoft is currently testing adding support for Intel�s Advanced Performance Extensions, which should yield improved 64bit performance and reduced power consumption. It makes sense to assume this support will be coming with Windows 11 27H2, which should hopefully lead to tangible performance improvements across the board. Also, there�s going to be a new default wallpaper. Be still my beating heart.
- The Ubuntu 26.04 Rust sudo is not compatible with standard sudo
Ubuntu has been at the forefront of replacing the traditional versions of basic tools like sudo with replacements written in Rust, but aside from worries about replacing battle-tested code with brand new, relatively untested code, there�s new things to worry about it. As it turns out, sudo-rs, the Rust replacement for sudo, is intentionally incompatible with the classic version in dangerous ways, as Chris Siebenmann discovered to his dismay. Basically, the classic sudo supports the use of wildcards defined using square brackets, so that if you allow a user to run, say, /usr/sbin/exim -bp, without a password, they can run exim -bpa, exim -bpc, exim -bpr, or exim -bpu without having to supply a password. This allows for very specific, fine-grained access control, which is quite a nice capability to have if you�re managing many systems and users. Sadly, sudo-rs intentionally does not support this, opting to only allow you to use the generic * wildcard. Worse yet, it doesn�t really make this clear, either. ↫ Chris Siebenmann I do not really have words for this. The Rust sudo has apparently opted to keep the single most dangerous wildcard while disallowing all of the wildcards that allow one to be narrow and specific about what you�re allowing, and it buries this at the end of a section that devotes a bunch of words to describing functionality it doesn�t have and doesn�t support, with absolutely nothing else in that section to say this (either up front or in the descriptions of how all the wildcards would work if sudo-rs supported them, which it doesn�t). If you�re going to replace such vital, core tools like sudo that god knows how many people rely on every single day, you better be damn sure you�re feature-complete and can act as a drop-in replacement. If someone switches from sudo to doas, nobody expects the experience to be identical. However, if you�re consistently being told that sudo-rs is a drop-in replacement and you shouldn�t expect any disruptions, you better be able to make true on that promise. Ubuntu isn�t some also-ran small hobby distribution, and its developers should act like it. What a clown show.
- LXQt 2.5.0 released
The second desktop environment release I�ve got for you today is LXQt 2.5.0. This new version excises its last LXDE dependency, and QTerminal and QTermWidget received considerable improvements, like new background image modes, a visual bell, support for OSC-8 hyperlinks, and more. There�s a ton of smaller changes and improvements as well, but do note that due to a bug, 2.5.0 broke LXQt�s Monitor Settings on X11. The project intends to fix this as quickly as possible and push a point release to address this issue.
- Cinnamon 6.8 desktop environment released with hibernation support
It�s desktop environment Thursday, as I�ve got two new releases for you today. First, Cinnamon, the desktop environment primarily associated with Linux Mint, has hit version 6.8. This version will officially ship with Linux Mint 27, scheduled for around Christmas of this year. Highlights of Cinnamon 6.8 include hibernation support via a Suspend action in the main menu, modern one-to-one trackpad gestures for both Wayland and Xorg sessions, support for the oo7 Secret Service provider, support for multiple instances in the Sound applet, and a more unified Network applet that merges the WireGuard and VPN sections. ↫ Marcus Nestor at 9To5Linux While Cinnamon is first and foremost a Linux Mint project, it�s available on countless other distributions as well, including dedicated variants for popular distributions like Fedora and Ubuntu. Its Wayland support is finally materialising too, which is long overdue.
- NetBSD 11.1 released
The first point release for NetBSD 11 has been released. As the version number suggests, there�s no major changes here. This release includes security updates for mozilla-rootcerts, brotli, xorg-server, hdaudio(4), compat_linux(8), unbound(8), and ipfilter. Among the non-security related changes are improved USB device stability on Raspberry Pi, fixed hot-plugging bugs in various USB Wi-Fi drivers, support for battery monitoring on the Microsoft Surface Go 3, fixed thread-local storage on ARMv5, fixes for running the MIPS Malta and PA-RISC ports under QEMU, support for the Zhaoxin KX-7000 CPU, and support for sensors, i2c, real-time clocks, and fan control on Sun Ultra 25/45 and Sun Fire V215/V245 machines. ↫ Nia Alarie on the NetBSD blog The full release notes provide more details.
- EU OS: A Bold Step Toward Digital Sovereignty for Europe
Image 
A new initiative, called "EU OS," has been launched to develop a Linux-based operating system tailored specifically for the public sector organizations of the European Union (EU). This community-driven project aims to address the EU's unique needs and challenges, focusing on fostering digital sovereignty, reducing dependency on external vendors, and building a secure, self-sufficient digital ecosystem.
What Is EU OS?
EU OS is not an entirely novel operating system. Instead, it builds upon a Linux foundation derived from Fedora, with the KDE Plasma desktop environment. It draws inspiration from previous efforts such as France's GendBuntu and Munich's LiMux, which aimed to provide Linux-based systems for public sector use. The goal remains the same: to create a standardized Linux distribution that can be adapted to different regional, national, and sector-specific needs within the EU.
Rather than reinventing the wheel, EU OS focuses on standardization, offering a solid Linux foundation that can be customized according to the unique requirements of various organizations. This approach makes EU OS a practical choice for the public sector, ensuring broad compatibility and ease of implementation across diverse environments.
The Vision Behind EU OS
The guiding principle of EU OS is the concept of "public money – public code," ensuring that taxpayer money is used transparently and effectively. By adopting an open-source model, EU OS eliminates licensing fees, which not only lowers costs but also reduces the dependency on a select group of software vendors. This provides the EU’s public sector organizations with greater flexibility and control over their IT infrastructure, free from the constraints of vendor lock-in.
Additionally, EU OS offers flexibility in terms of software migration and hardware upgrades. Organizations can adapt to new technologies and manage their IT evolution at a manageable cost, both in terms of finances and time.
However, there are some concerns about the choice of Fedora as the base for EU OS. While Fedora is a solid and reliable distribution, it is backed by the United States-based Red Hat. Some argue that using European-backed projects such as openSUSE or KDE's upcoming distribution might have aligned better with the EU's goal of strengthening digital sovereignty.
Conclusion
EU OS marks a significant step towards Europe's digital independence by providing a robust, standardized Linux distribution for the public sector. By reducing reliance on proprietary software and vendors, it paves the way for a more flexible, cost-effective, and secure digital ecosystem. While the choice of Fedora as the base for the project has raised some questions, the overall vision of EU OS offers a promising future for Europe's public sector in the digital age.
Source: It's FOSS
European Union
- Linus Torvalds Acknowledges Missed Release of Linux 6.14 Due to Oversight
Linus Torvalds Acknowledges Missed Release of Linux 6.14 Due to Oversight
Linux kernel lead developer Linus Torvalds has admitted to forgetting to release version 6.14, attributing the oversight to his own lapse in memory. Torvalds is known for releasing new Linux kernel candidates and final versions on Sunday afternoons, typically accompanied by a post detailing the release. If he is unavailable due to travel or other commitments, he usually informs the community ahead of time, so users don’t worry if there’s a delay.
In his post on March 16, Torvalds gave no indication that the release might be delayed, instead stating, “I expect to release the final 6.14 next weekend unless something very surprising happens.” However, Sunday, March 23rd passed without any announcement.
On March 24th, Torvalds wrote in a follow-up message, “I’d love to have some good excuse for why I didn’t do the 6.14 release yesterday on my regular Sunday afternoon schedule,” adding, “But no. It’s just pure incompetence.” He further explained that while he had been clearing up unrelated tasks, he simply forgot to finalize the release. “D'oh,” he joked.
Despite this minor delay, Torvalds’ track record of successfully managing the Linux kernel’s development process over the years remains strong. A single day’s delay is not critical, especially since most Linux users don't urgently need the very latest version.
The new 6.14 release introduces several important features, including enhanced support for writing drivers in Rust—an ongoing topic of discussion among developers—support for Qualcomm’s Snapdragon 8 Elite mobile chip, a fix for the GhostWrite vulnerability in certain RISC-V processors from Alibaba’s T-Head Semiconductor, and a completed NTSYNC driver update that improves the WINE emulator’s ability to run Windows applications, particularly games, on Linux.
Although the 6.14 release went smoothly aside from the delay, Torvalds expressed that version 6.15 may present more challenges due to the volume of pending pull requests. “Judging by my pending pile of pull requests, 6.15 will be much busier,” he noted.
You can download the latest kernel here.
Linus Torvalds kernel
- AerynOS 2025.03 Alpha Released with GNOME 48, Mesa 25, and Linux Kernel 6.13.8
Image 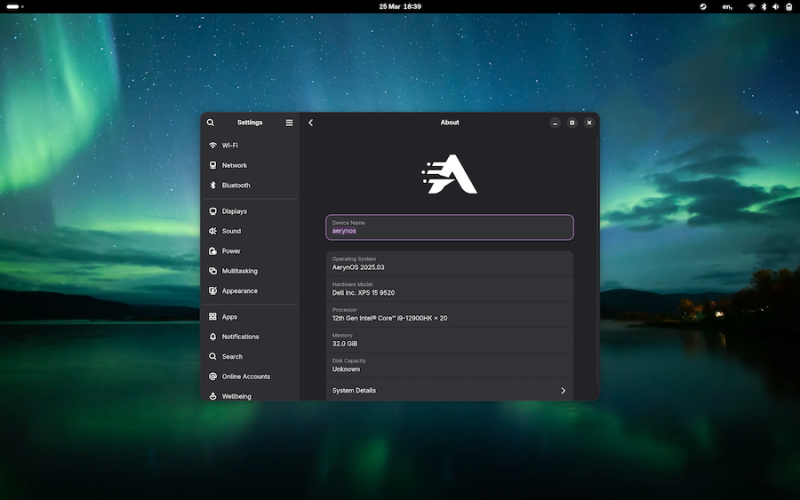
AerynOS 2025.03 has officially been released, introducing a variety of exciting features for Linux users. The release includes the highly anticipated GNOME 48 desktop environment, which comes with significant improvements like HDR support, dynamic triple buffering, and a Wayland color management protocol. Other updates include a battery charge limiting feature and a Wellbeing option aimed at improving user experience.
This release, while still in alpha, incorporates Linux kernel 6.13.8 and the updated Mesa 25.0.2 graphics stack, alongside tools like LLVM 19.1.7 and Vulkan SDK 1.4.309.0. Additionally, the Moss package manager now integrates os-info to generate more detailed OS metadata via a JSON file.
Future plans for AerynOS include automated package updates, easier rollback management, improved disk handling with Rust, and fractional scaling enabled by default. The installer has also been revamped to support full disk wipes and dynamic partitioning.
Although still considered an alpha release, AerynOS 2025.03 can be downloaded and tested right now from its official website.
Source: 9to5Linux
AerynOS
- Xojo 2025r1: Big Updates for Developers with Linux ARM Support, Web Drag and Drop, and Direct App Store Publishing
Image 
Xojo has just rolled out its latest release, Xojo 2025 Release 1, and it’s packed with features that developers have been eagerly waiting for. This major update introduces support for running Xojo on Linux ARM, including Raspberry Pi, brings drag-and-drop functionality to the Web framework, and simplifies app deployment with the ability to directly submit apps to the macOS and iOS App Stores.
Here’s a quick overview of what’s new in Xojo 2025r1:
1. Linux ARM IDE Support
Xojo 2025r1 now allows developers to run the Xojo IDE on Linux ARM devices, including popular platforms like Raspberry Pi. This opens up a whole new world of possibilities for developers who want to create apps for ARM-based devices without the usual complexity. Whether you’re building for a Raspberry Pi or other ARM devices, this update makes it easier than ever to get started.
2. Web Drag and Drop
One of the standout features in this release is the addition of drag-and-drop support for web applications. Now, developers can easily drag and drop visual controls in their web projects, making it simpler to create interactive, user-friendly web applications. Plus, the WebListBox has been enhanced with support for editable cells, checkboxes, and row reordering via dragging. No JavaScript required!
3. Direct App Store Publishing
Xojo has also streamlined the process of publishing apps. With this update, developers can now directly submit macOS and iOS apps to App Store Connect right from the Xojo IDE. This eliminates the need for multiple steps and makes it much easier to get apps into the App Store, saving valuable time during the development process.
4. New Desktop and Mobile Features
This release isn’t just about web and Linux updates. Xojo 2025r1 brings some great improvements for desktop and mobile apps as well. On the desktop side, all projects now include a default window menu for macOS apps. On the mobile side, Xojo has introduced new features for Android and iOS, including support for ColorGroup and Dark Mode on Android, and a new MobileColorPicker for iOS to simplify color selection.
5. Performance and IDE Enhancements
Xojo’s IDE has also been improved in several key areas. There’s now an option to hide toolbar captions, and the toolbar has been made smaller on Windows. The IDE on Windows and Linux now features modern Bootstrap icons, and the Documentation window toolbar is more compact. In the code editor, developers can now quickly navigate to variable declarations with a simple Cmd/Ctrl + Double-click. Plus, performance for complex container layouts in the Layout Editor has been enhanced.
What Does This Mean for Developers?
Xojo 2025r1 brings significant improvements across all the platforms that Xojo supports, from desktop and mobile to web and Linux. The added Linux ARM support opens up new opportunities for Raspberry Pi and ARM-based device development, while the drag-and-drop functionality for web projects will make it easier to create modern, interactive web apps. The ability to publish directly to the App Store is a game-changer for macOS and iOS developers, reducing the friction of app distribution.
How to Get Started
Xojo is free for learning and development, as well as for building apps for Linux and Raspberry Pi. If you’re ready to dive into cross-platform development, paid licenses start at $99 for a single-platform desktop license, and $399 for cross-platform desktop, mobile, or web development. For professional developers who need additional resources and support, Xojo Pro and Pro Plus licenses start at $799. You can also find special pricing for educators and students.
Download Xojo 2025r1 today at xojo.com.
Final Thoughts
With each new release, Xojo continues to make cross-platform development more accessible and efficient. The 2025r1 release is no exception, delivering key updates that simplify the development process and open up new possibilities for developers working on a variety of platforms. Whether you’re a Raspberry Pi enthusiast or a mobile app developer, Xojo 2025r1 has something for you.
Xojo ARM
- New 'Mirrored' Network Mode Introduced in Windows Subsystem for Linux
Microsoft's Windows Subsystem for Linux (WSL) continues to evolve with the release of WSL 2 version 0.0.2. This update introduces a set of opt-in preview features designed to enhance performance and compatibility.
Key additions include "Automatic memory reclaim" which dynamically optimizes WSL's memory footprint, and "Sparse VHD" to shrink the size of the virtual hard disk file. These improvements aim to streamline resource usage.
Additionally, a new "mirrored networking mode" brings expanded networking capabilities like IPv6 and multicast support. Microsoft claims this will improve VPN and LAN connectivity from both the Windows host and Linux guest.
Complementing this is a new "DNS Tunneling" feature that changes how DNS queries are resolved to avoid compatibility issues with certain network setups. According to Microsoft, this should reduce problems connecting to the internet or local network resources within WSL.
Advanced firewall configuration options are also now available through Hyper-V integration. The new "autoProxy" feature ensures WSL seamlessly utilizes the Windows system proxy configuration.
Microsoft states these features are currently rolling out to Windows Insiders running Windows 11 22H2 Build 22621.2359 or later. They remain opt-in previews to allow testing before final integration into WSL.
By expanding WSL 2 with compelling new capabilities in areas like resource efficiency, networking, and security, Microsoft aims to make Linux on Windows more performant and compatible. This evolutionary approach based on user feedback highlights Microsoft's commitment to WSL as a key part of the Windows ecosystem.
Windows
- Linux Threat Report: Earth Lusca Deploys Novel SprySOCKS Backdoor in Attacks on Government Entities
The threat actor Earth Lusca, linked to Chinese state-sponsored hacking groups, has been observed utilizing a new Linux backdoor dubbed SprySOCKS to target government organizations globally.
As initially reported in January 2022 by Trend Micro, Earth Lusca has been active since at least 2021 conducting cyber espionage campaigns against public and private sector targets in Asia, Australia, Europe, and North America. Their tactics include spear-phishing and watering hole attacks to gain initial access. Some of Earth Lusca's activities overlap with another Chinese threat cluster known as RedHotel.
In new research, Trend Micro reveals Earth Lusca remains highly active, even expanding operations in the first half of 2023. Primary victims are government departments focused on foreign affairs, technology, and telecommunications. Attacks concentrate in Southeast Asia, Central Asia, and the Balkans regions.
After breaching internet-facing systems by exploiting flaws in Fortinet, GitLab, Microsoft Exchange, Telerik UI, and Zimbra software, Earth Lusca uses web shells and Cobalt Strike to move laterally. Their goal is exfiltrating documents and credentials, while also installing additional backdoors like ShadowPad and Winnti for long-term spying.
The Command and Control server delivering Cobalt Strike was also found hosting SprySOCKS - an advanced backdoor not previously publicly reported. With roots in the Windows malware Trochilus, SprySOCKS contains reconnaissance, remote shell, proxy, and file operation capabilities. It communicates over TCP mimicking patterns used by a Windows trojan called RedLeaves, itself built on Trochilus.
At least two SprySOCKS versions have been identified, indicating ongoing development. This novel Linux backdoor deployed by Earth Lusca highlights the increasing sophistication of Chinese state-sponsored threats. Robust patching, access controls, monitoring for unusual activities, and other proactive defenses remain essential to counter this advanced malware.
The Trend Micro researchers emphasize that organizations must minimize attack surfaces, regularly update systems, and ensure robust security hygiene to interrupt the tactics, techniques, and procedures of relentless threat groups like Earth Lusca.
Security
- Linux Kernel Faces Reduction in Long-Term Support Due to Maintenance Challenges
The Linux kernel is undergoing major changes that will shape its future development and adoption, according to Jonathan Corbet, Linux kernel developer and executive editor of Linux Weekly News. Speaking at the Open Source Summit Europe, Corbet provided an update on the latest Linux kernel developments and a glimpse of what's to come.
A major change on the horizon is a reduction in long-term support (LTS) for kernel versions from six years to just two years. Corbet explained that maintaining old kernel branches indefinitely is unsustainable and most users have migrated to newer versions, so there's little point in continuing six years of support. While some may grumble about shortened support lifecycles, the reality is that constantly backporting fixes to ancient kernels strains maintainers.
This maintainer burnout poses a serious threat, as Corbet highlighted. Maintaining Linux is largely a volunteer effort, with only about 200 of the 2,000+ developers paid for their contributions. The endless demands on maintainers' time from fuzz testing, fixing minor bugs, and reviewing contributions takes a toll. Prominent maintainers have warned they need help to avoid collapse. Companies relying on Linux must realize giving back financially is in their interest to sustain this vital ecosystem.
The Linux kernel is also wading into waters new with the introduction of Rust code. While Rust solves many problems, it also introduces new complexities around language integration, evolving standards, and maintainer expertise. Corbet believes Rust will pass the point of no return when core features depend on it, which may occur soon with additions like Apple M1 GPU drivers. Despite skepticism in some corners, Rust's benefits likely outweigh any transition costs.
On the distro front, Red Hat's decision to restrict RHEL cloning sparked community backlash. While business considerations were at play, Corbet noted technical factors too. Using older kernels with backported fixes, as RHEL does, risks creating divergent, vendor-specific branches. The Android model of tracking mainline kernel dev more closely has shown security benefits. Ultimately, Linux works best when aligned with the broader community.
In closing, Corbet recalled the saying "Linux is free like a puppy is free." Using open source seems easy at first, but sustaining it long-term requires significant care and feeding. As Linux is incorporated into more critical systems, that maintenance becomes ever more crucial. The kernel changes ahead are aimed at keeping Linux healthy and vibrant for the next generation of users, businesses, and developers.
kernel
- Linux Celebrates 32 Years with the Release of 6.6-rc2 Version
Today marks the 32nd anniversary of Linus Torvalds introducing the inaugural Linux 0.01 kernel version, and celebrating this milestone, Torvalds has launched the Linux 6.6-rc2. Among the noteworthy updates are the inclusion of a feature catering to the ASUS ROG Flow X16 tablet's mode handling and the renaming of the new GenPD subsystem to pmdomain.
The Linux 6.6 edition is progressing well, brimming with exciting new features that promise to enhance user experience. Early benchmarks are indicating promising results, especially on high-core-count servers, pointing to a potentially robust and efficient update in the Linux series.
Here is what Linus Torvalds had to say in today's announcement:
Another week, another -rc.I think the most notable thing about 6.6-rc2 is simply that it'sexactly 32 years to the day since the 0.01 release. And that's a roundnumber if you are a computer person.Because other than the random date, I don't see anything that reallystands out here. We've got random fixes all over, and none of it looksparticularly strange. The genpd -> pmdomain rename shows up in thediffstat, but there's no actual code changes involved (make sure touse "git diff -M" to see them as zero-line renames).And other than that, things look very normal. Sure, the architecturefixes happen to be mostly parisc this week, which isn't exactly theusual pattern, but it's also not exactly a huge amount of changes.Most of the (small) changes here are in drivers, with some tracingfixes and just random things. The shortlog below is short enough toscroll through and get a taste of what's been going on. Linus Torvalds
- Introducing Bavarder: A User-Friendly Linux Desktop App for Quick ChatGPT Interaction
Want to interact with ChatGPT from your Linux desktop without using a web browser?
Bavarder, a new app, allows you to do just that.
Developed with Python and GTK4/libadwaita, Bavarder offers a simple concept: pose a question to ChatGPT, receive a response, and promptly copy the answer (or your inquiry) to the clipboard for pasting elsewhere.
With an incredibly user-friendly interface, you won't require AI expertise (or a novice blogger) to comprehend it. Type your question in the top box, click the blue send button, and wait for a generated response to appear at the bottom. You can edit or modify your message and repeat the process as needed.
During our evaluation, Bavarder employed BAI Chat, a GPT-3.5/ChatGPT API-based chatbot that's free and doesn't require signups or API keys. Future app versions will incorporate support for alternative backends, such as ChatGPT 4 and Hugging Chat, and allow users to input an API key to utilize ChatGPT3.
At present, there's no option to regenerate a response (though you can resend the same question for a potentially different answer). Due to the lack of a "conversation" view, tracking a dialogue or following up on answers can be challenging — but Bavarder excels for rapid-fire questions.
As with any AI, standard disclaimers apply. Responses might seem plausible but could contain inaccurate or false information. Additionally, it's relatively easy to lead these models into irrational loops, like convincing them that 2 + 2 equals 106 — so stay alert!
Overall, Bavarder is an attractive app with a well-defined purpose. If you enjoy ChatGPT and similar technologies, it's worth exploring.
ChatGPT AI
- LibreOffice 7.5.3 Released: Third Maintenance Update Brings 119 Bug Fixes to Popular Open-Source Office Suite
Today, The Document Foundation unveiled the release and widespread availability of LibreOffice 7.5.3, which serves as the third maintenance update to the current LibreOffice 7.5 open-source and complimentary office suite series.
Approximately five weeks after the launch of LibreOffice 7.5.2, LibreOffice 7.5.3 arrives with a new set of bug fixes for those who have successfully updated their GNU/Linux system to the LibreOffice 7.5 series.
LibreOffice 7.5.3 addresses a total of 119 bugs identified by users or uncovered by LibreOffice developers. For a more comprehensive understanding of these bug fixes, consult the RC1 and RC2 changelogs.
You can download LibreOffice 7.5.3 directly from the LibreOffice website or from SourceForge as binary installers for DEB or RPM-based GNU/Linux distributions. A source tarball is also accessible for individuals who prefer to compile the software from sources or for system integrators.
All users operating the LibreOffice 7.5 office suite series should promptly update their installations to the new point release, which will soon appear in the stable software repositories of your GNU/Linux distributions.
In early February 2023, LibreOffice 7.5 debuted as a substantial upgrade to the widely-used open-source office suite, introducing numerous features and improvements. These enhancements encompass major upgrades to dark mode support, new application and MIME-type icons, a refined Single Toolbar UI, enhanced PDF Export, and more.
Seven maintenance updates will support LibreOffice 7.5 until November 30th, 2023. The next point release, LibreOffice 7.5.4, is scheduled for early June and will include additional bug fixes.
The Document Foundation once again emphasizes that the LibreOffice office suite's "Community" edition is maintained by volunteers and members of the Open Source community. For enterprise implementations, they suggest using the LibreOffice Enterprise family of applications from ecosystem partners.
LibreOffice
|