|
1825 Monetary Lane Suite #104 Carrollton, TX
Do a presentation at NTLUG.
What is the Linux Installation Project?
Real companies using Linux!
Not just for business anymore.
Providing ready to run platforms on Linux
|
Show Descriptions... (Show All/All+Images)
(Single Column)
- [$] A new generation of futexes
Futexesare a kernel subsystem that provides support for fast mutexesin user space. While futexes can indeed be fast, they are not fast enoughfor a number of users. Partly as a result of that, the implementation offutexes has grown in complexity over the years, with two basic variantson offer. The desire for faster futexes remains, though, and that inspiresnew patches, including this seriesfrom Suleiman Souhlal adding a third futex class called "futex PING"for "priority inheritance next generation".
- Manjaro Project e.V. non-profit organization created
Frank Vandermeiren has announcedthe creation of the Manjaro Project e.V., a nonprofit organization in Germanythat is independent of the Manjaro GmbH & Co KG company. This is following a governance struggle that took placeearlier this year between a number of ManjaroLinux contributors and Philip Müller, project lead and CEO of the Manjarocompany.
At the moment, we are still working on optimizing the new developmentinfrastructure, which was partly necessitated by the ongoing (A.I.) bot attacksagainst our old infrastructure.
However, as you may have noticed, the last TestingUpdates and StableUpdates were initiated by the Manjaro Team without supervision from PhilipMüller — with special thanks to @Yochanan for his hard work!
Dennis ten Hoove has indicatedthat "a transfer of company assets to the e.V. has not yet taken place",and the group's next step is to ready the nonprofit for the transition and"reach out and engage in dialogue with the company".
- Security updates for Monday
Security updates have been issued by Debian (freedombox, kernel, libspreadsheet-xlsx-perl, network-manager-iodine, pdns-recursor, postgresql-15, radsecproxy, and sogo), Fedora (afflib, asahi-installer, below, cloc, dhcpcd, dnf5, epiphany, firefox, glib-networking, hugo, mingw-python3, mtools, mysql8.4, mysql9.7, proftpd, python-cramjam, python-fastar, python-h5io, python-PyMuPDF, python-uv-build, radicale, rubygem-loofah, rubygem-nokogiri, rust-archive-trait, rust-askalono-cli, rust-astral-html, rust-cargo-deny, rust-libcramjam0.8, rust-onefetch, rust-ptools, rust-sccache, rustup, uv, and xorg-x11-server), Gentoo (Apache HTTPD, rsync, and Tor), Oracle (cockpit, firefox, grafana, grafana-pcp, gstreamer1, gstreamer1-plugins-base, kernel, kernel-uek, mingw-libpng, nginx:1.24, perl-CGI, python3, qt5-qtbase, qt5-qtdeclarative, webkit2gtk3, xfsprogs, and xorg-x11-server), and SUSE (389-ds, aliyun-cli, amazon-ssm-agent, apache2, binutils, brotli, bun, cadvisor, chromium, gn, distribution-registry, evolution, firefox, firefox-esr, fleet-cli, fortio, gosec, hauler, hawk-apiserver, hawk2, helmsman, hugo, java-17-openjdk, jsoup, k3sup, kdeconnect-kde, kernel, krb5, kubectl-retina, kubelogin, kubeseal, kumactl, libosmocore, libyang-devel, patch, perl-mozilla-ca, pinact, prometheus-ha_cluster_exporter, python-brotli, python-graphql-core, python-Pillow, python313-Brotli, python313-pypdf, python313-uv, rqlite, rsyslog, scribus, sdbootutil-1, timoni, trivy, vifm, and warewulf4).
- Kernel prepatch 7.4-rc3
The 7.4-rc3 kernel prepatch is out fortesting. Linus declared: "It looks fairly normal, with drivers(networking and gpu) leading the charge. There's lots and lots of changes,but most of the actual patches are tiny."
- [$] 25 years of Buildroot
Buildroot maintainer Peter Korsgaardgave a presentation about the long history of the build tool for embeddedLinux systems at the 2026 EmbeddedLinux Conference Europe. In it, he covered more than just the past 25years, looking at the current status of the project as well as what toexpect in Buildroot's future. It was an interesting view inside this long-running project thathas been a mainstay of the embedded-Linux world throughout almost all ofthis century.
- Announcing XRAID: declustered parity RAID for zoned XFS
Christoph Hellwig has announced theinitial public release of XRAID—declustered parity RAID that is integratedinto XFS.
The two primary aims of XRAID are to support parity RAID on zoned deviceslike SMR hard drives, and to provide a fast RAID implementation withoutinherent data integrity problems. XRAID, just like zoned XFS also workson conventional hard drives and SSDs. Optimizing for SSD performance hasnot been a focus, but even without that, writes are up to 20 times fasterthan mdraid. [...]
Work on XRAID has been ongoing for a year and a half, and while we aren'tanywhere near ready for an upstream submission, we are interested infeedback and testing from a wider audience now. The currentimplementation supports zero to 2 parities. We did experiments with theSnapRAID parity library to support 3 and more parities, and while thatis not included in the current version, support for more parities isplanned and the code is prepared for it.
The xfsprogs branch includes mkfs support and a new "xraid" utility formanaging devices and inspecting an XRAID file-systems. We have alsoextended Zonar (The zoned file-system visualisation tool) to show howeach logical zone maps onto physical zones on devices.
Hellwig gave a presentation atFOSSY in August on this topic; video of the talk does not seem to be availableyet, but his slides areavailable.
- Security updates for Friday
Security updates have been issued by AlmaLinux (.NET 10.0, .NET 8.0, .NET 9.0, firefox, gcc, grafana, grafana-pcp, gstreamer1, gstreamer1-plugins-base, java-1.8.0-openjdk, kernel, kernel-rt, libimobiledevice, mingw-libpng, nginx:1.24, nodejs:22, nodejs:24, perl-CGI, perl-DBI, qt5-qtbase, tigervnc, vim, and xorg-x11-server), Debian (apache2, c-ares, linux-6.12, node-shell-quote, nova, parted, postgresql-17, python-django, sympa, and tomcat10), Fedora (cockpit, erlang-ssl_verify_fun, httpd, ignition, jackson-bom, jackson-core, jackson-databind, jackson-modules-base, libvirt, mod_http2, mongo-c-driver, poppler, prometheus, pylint, python-discovery, python-loguru, python-PyMuPDF, rabbitmq-server, rust-crypto-bigint, rust-ctutils, rust-elliptic-curve, rust-num-bigint, rust-num-bigint0.4, rust-num-modular, rust-num-modular0.6, rust-num-prime, rust-routinator, rust-zmij, strongswan, xen, xorg-x11-server, and zvbi), Mageia (amule, peazip, and python-pytest), Red Hat (buildah, fence-agents, go-fdo-server, grafana, grafana-pcp, oci-seccomp-bpf-hook, osbuild-composer, podman, and rhc), SUSE (ansible-core, apr-util, aspell, brotli, cadvisor, civetweb, distribution-registry, elemental, elemental-register,, elemental-operator, elemental-system-agent, elemental- toolkit, ffmpeg, firefox, gimp, git-annex, go1.26, go1.27, golang-github-prometheus-prometheus, google-cloud-sap-agent, google-guest-agent, google-osconfig-agent, goose, gosec, graphicsmagick, haproxy, hauler, hawk-apiserver, hawk2, hcloud-cli, jhead, jsoup, kernel, librsvg, libXtst, libxtst, nodejs24, nvidia-open-driver-G07-signed, nvidia-open-driver-g07-signed, open-iscsi, perl-XS-Parse-Keyword, perl-xs-parse-keyword, python-asyncssh, python-Brotli, python-django, python-joserfc, python-M2Crypto, python-Pillow, python-pillow, python313-setuptools, rsyslog, speex, tiff, trivy, udisks2, vsftpd, xen, and xorg-x11-server), and Ubuntu (apache2, charybdis, debian-lan-config, glibc, golang-github-seccomp-libseccomp-golang, hiredis, httpie, imapfilter, lhasa, libjgraphx-java, libjwt, libsolv, linux-fips, linux-hwe-6.8, linux-hwe-7.0, linux-nvidia-tegra, minissdpd, ncmpc, nfdump, node-tough-cookie, openconnect, pillow, pngquant, python-gevent, radicale, ruby-openid, sa-exim, signing-party, sudo, tigervnc, and x11vnc).
- Glasswing overwhelms maintainers with underwhelming findings (VulnCheck)
Patrick Garrity of VulnCheck has written a blogpost that looks at vulnerabilities found by Anthropic's Project Glasswing since itlaunched on April 7, and finds it wanting:
Of the 37,966 findings Anthropic reports, only 7,349 (19.4%) have been madepublic. Just 217 of those have been marked fixed. The more glaring number isthat 4.4% (1,654) of the project's findings have already been marked asduplicates, 7.5x more duplicates than fixes. On top of that, 419 findings havebeen withdrawn. It seems odd that the ledger now claims a 94.2% true positiverate, up from 90.8% at launch, when more findings have been withdrawn or markedas duplicates than fixed, likely a feedback loop missing to the triage rateslisted as "True Positives".
[...] AI is a valuable tool for finding vulnerabilities, and I'm notdiscounting that. But seven months in, the evidence still doesn't match thelaunch narrative. The CVEs are a sliver of this year's total, almost none arebeing exploited, fixes have stalled while duplicates and withdrawals pile up,and the triage burden is shifting onto the open source maintainers Glasswingpromised to help. The receipts keep coming in. They still don't reconcile.
- Introducing Polo: a Wayland MATE compositor
Kerem Söke has announcedthe 1.0release of Polo, aWayland compositor for the MATE DesktopEnvironment:
The idea is to keep MATE behaving as closely as possible to how it does onX11, rather than changing the desktop to fit a different compositor. [...]
Window management, metacity, workspaces, tiling, XWayland, clipboard andclipman support, multiple monitors, display scaling, hotplugging, screenshots,screen sharing, and session management are all working.
I've also added desktop effects: fade, zoom, zap, spin, squeemize, magiclamp, desktop cube, expo, and wobbly windows.
Söke is looking for people to test Polo, particularly on multi-monitorsetups, and report back with problems.

- Euro-Office Is Here � As Nextcloud Office Desktop
Online Euro-Office arrived this summer for running on Nextcloud�s platform, but now a version that runs locally has been released for Linux, Mac, and Windows � and it�s ready to collaborate with the cloud version.
- MRDIMM 8800 MT/s vs. 12800 MT/s Memory Performance With AMD EPYC Venice
With last week's AMD EPYC 9006 SP7 availability and the AMD EPYC 9686F and EPYC 9996 processor reviews, one of the most frequent questions/comments was around the impact that the new MRDIMM-12800 memory had on these Zen 6 server processors compared to prior gen and the Intel/NVIDIA server competition. Given that curiosity over the MRDIMM-12800 impact, here are the EPYC 9686F 2P benchmarks when0
- Snap Store saw several hundred new apps added in one weekend
Canonical�s Snap Store has seen a huge uptick in app uploads over the past few days � one account publishing more than 100 utilities and games in 24 hours. What gives? Is the snap store finally seeing a second wind? Typically, the snap store sees between 15-30 new app uploads (not updates) a day, per a quick eyeball of the �new� graph on Alan Pope�s SnapUpdates site. But since the 13 November0
- California Sues OpenAI Over Hugging Face, Other AI Model Loss of Control
"California's attorney general just sued OpenAI," writes longtime Slashdot reader destinyland. "The action accuses OpenAI of putting public safety at risk, reports CNBC, specifically by its past failures to contain its AI models within their testing environments." From the report: [California Attorney General Rob Bonta] cited the "infamous" incident in July, where two OpenAI models broke out of a testing environment, gained unauthorized access to the open internet, and breached the internal systems of open-source developer platform Hugging Face. OpenAI said the models were trying to find information that they could use to cheat on an evaluation, and succeeded. The break-in at Hugging Face, which Nvidia acquired for roughly $13 billion in September, rattled industry researchers and prompted government officials to call for more stringent oversight of the AI industry. On Monday, Bonta said that OpenAI later disclosed to his investigators that it was aware of 80 incidents "involving loss of control and access to third-party networks and websites." "But the company failed to provide the detailed information we requested to evaluate these incidents; this is concerning, and it puts the public at risk," he said. Bonta's suit, filed in state Superior Court in San Francisco, alleges OpenAI violated California's Unfair Competition Law and accuses the company of being a public nuisance as defined by state law. The attorney general told reporters he believed in AI's technological power, and the potential of AI models to "achieve scientific breakthroughs, boost economic growth, guard against cyber attacks, and benefit all Californians." "But AI systems must be developed and designed safely," he said. "The companies that develop these models have a moral and yes, a legal responsibility to keep public safety at the forefront." The lawsuit can be found here (PDF).
 
Read more of this story at Slashdot.
- Just 400 US Data Centers Use More Electricity Than Michigan
An anonymous reader quotes a report from Wired: Just 400 hyperscale data centers connected in the US used as much electricity as the state of Michigan in a single year, new Harvard research has found. The study, published Monday in Nature Sustainability, also finds that the majority of that electricity was generated using fossil fuels, and data center emissions are three times higher than they were before the AI boom. Federal and state governments do not track data center use separate from the rest of the power sector, despite mounting projections that data centers are putting serious strain on the American power grid. Individual data centers' power use is often considered proprietary business information, and data center operators and utilities do not have to disclose specific numbers to the public. The Harvard study specifically focuses on hyperscale data centers -- the largest types of facilities, which have become flashpoints in community opposition across the country. While often used for AI inference or training, not all of the hyperscalers surveyed in this study are being used for AI. [...] To assemble their dataset, the Harvard researchers put together a list of 403 hyperscale data centers around the country that were operational between May 2024 and April 2025 using a mix of industry research and satellite data. The team then modeled these facilities' energy use in a variety of scenarios and calculated the energy mix of the regional grids to estimate individual facilities' carbon emissions. Not all regions were created equal: Data centers in Virginia, Oregon, Ohio, and Iowa -- the first of which is home to Data Center Alley -- were responsible for more than 50 percent of the energy use in the study. The report notes that these findings may already be outdated. "Some of the massive campuses being proposed today are substantially larger than the typical facility in our dataset," says Gianluca Guidi, a postdoctoral research fellow at Harvard's T. H. Chan School of Public Health and the lead author of the study. The study also excludes onsite power generation, a rapidly growing trend that BloombergNEF estimates could increase overall U.S. emissions by 10% if all proposed projects are built.
Read more of this story at Slashdot.
- JPMorgan Chase Glitch Disrupts Online Banking Across Major US Banks
A software bug at JPMorgan Chase has disrupted online banking services Monday, triggering transaction delays for thousands of customers at Chase and other major U.S. banks. "JPMorgan Chase has experienced a temporary issue related to a software bug in an on-premise hardware system -- it is not cyber-related," said Joe Evangelisti, spokesman for the bank. "This is not a systemic issue -- other banks may have been impacted by slowness in transactions only to the extent that they were a party to a transaction with us," he added. The Associated Press reports: Monday's technical issues seem to be centered at Chase customers and customers at other banks trying to transact with Chase. Those banks, including Bank of America and Citigroup, were not having issues with their banking services. A spokesman for U.S. Bank said its systems are not directly impacted but that "clients attempting to send or receive Zelle payments with another financial institution may experience transaction delays." Developing...
Read more of this story at Slashdot.
- Comcast's 'Fiber-Powered Wi-Fi' Is Just Cable, AT&T Says In False Advertising Case
AT&T is suing (PDF) Comcast over its "fiber-powered" advertising, arguing that the term misleads consumers into believing Xfinity offers fiber-to-the-home service when most customers actually receive their Internet through coaxial cable. "Comcast should be required to restore to AT&T any and all profits earned as a result of its false and misleading advertising or provide AT&T with any other restitutionary relief the Court deems appropriate," the lawsuit said. The lawsuit asked for a permanent injunction "requiring Comcast to cease describing its hybrid fiber-coaxial service as 'Fiber-Powered.'" Ars Technica reports: While Comcast has deployed plenty of fiber throughout the US, its cable Internet service makes the final connection to homes with coaxial cable. This results in upload speeds being far slower than download speeds. In contrast, fiber-to-the-home service can provide symmetrical upload and download speeds. Comcast has deployed fiber-to-the-home in only small portions of its cable territory while advertising its service as fiber-powered in the majority of areas where cable makes the final connection. AT&T's lawsuit said that in describing its cable broadband as fiber-powered, Comcast "conveys to reasonable consumers the misleading impression that Xfinity Internet is a fiber-to-the-home service comparable to AT&T Fiber. In fact, the vast majority of Xfinity Internet runs over a hybrid fiber-coaxial ('HFC') network, where the critical 'last mile' connection to the customer's home uses copper coaxial cable, not fiber." [...] AT&T previously challenged Comcast's fiber-powered claims through the advertising industry's self-regulatory system operated by BBB National Programs' National Advertising Division (NAD). The NAD determined in June that Comcast accurately described its mix of cable and fiber technology in a disclosure, but that Comcast didn't make the disclosure prominently enough. [...] The NAD recommended that Comcast make the disclosure "more prominent and more proximate to the 'fiber-powered' Wi-Fi claim as necessary to ensure that the disclosure is clear and conspicuous." Comcast said it would comply with the decision, but AT&T's lawsuit makes it clear that it isn't satisfied with the current state of Comcast's advertising. We contacted Comcast and will update this article if it provides a response.
Read more of this story at Slashdot.
- FBI Says Artex AI Open-Source Hacking Tool Used to Breach Networks In 'Under Three Hours'
The FBI is warning (PDF) that hackers are using the AI-powered penetration-testing tool Artex to compromise networks in "under three hours" in some cases. The tool has been linked to attacks against South Korean financial institutions, at least 2,250 ConnectWise customers and Barracuda. TechCrunch reports: Artex is one of several open-source AI-powered penetration testing platforms, a category of software built to probe a network's defenses. Hackers can connect Artex to hosted frontier large language models (LLMs) like those from Anthropic and OpenAI, as well as to open-source models and non-U.S. models. The FBI says Artex intrusions can be "noisy," meaning they generate reams of traffic and data that may trigger a targeted company's defensive alerts. But the tools allow hackers to move at speeds that makes it far more harder for human defenders to keep up. In some cases, Artex-linked attacks can move from targeting a system to active compromise "in under three hours." Oftentimes, Artex will rely on rapidly scanning a victim's network to look for signs of weakness, and then exploit simple security bugs, such as weak protections and exposed or stolen passwords to gain a foothold. From there, Artex allows the hacker to spread across the network for databases, mailboxes, and other sensitive information. [...] After Artex was used in cyberattacks, the tool's developer made the software closed-source to prevent further attacks. But the FBI says the previous open-source version continues to circulate and remains "widely accessible" for use in cyberattacks. It's not only companies and targeted victims that have been compromised as a result of weakened security exploited by AI tools; the tools themselves have been exposed as well, potentially allowing outsiders to access powerful hacking capabilities. Last week, researchers found hundreds of publicly exposed Artex systems online, which had been placed on the internet without a password, likely by mistake or misconfiguration -- including the Artex system that was used to target South Korea.
Read more of this story at Slashdot.
- Microsoft Outage Leads To Chlorine Gas Poisoning At German Theme Park
Slashdot readers djgl and Mirnotoriety shared a story about how a Microsoft Outlook outage contributed to a chlorine leak at Germany's Phantasialand theme park, injuring 15 guests, four of whom were hospitalized. German broadcasting institution WDR reports (translated to English): We were all affected by this problem: On Friday, there was a disruption that crippled the US software company Microsoft, including its email program Outlook. Phantasialand was also affected. Due to the disruption, no emails were received, as the company informed WDR on Saturday. As a result, no one was aware that the sauna area's maintenance safety system had already issued an email alert. This was because the automatic dosing system had pumped too much chlorine into the pool. Guests at the Hotel Ling Bao in Phantasialand, Bruhl, were injured as a result. They complained of health problems after visiting the pool. The pool was temporarily closed but has since been reopened, as the fire department informed WDR on Saturday. Due to complaints from hotel guests, emergency services and the fire department were called. Thirteen guests complained of respiratory irritation; ultimately, the number of affected individuals rose to a total of 15. Cybersecurity architect and computer scientist Stephan Skrobisch said Microsoft is not responsible for the incident. "It's clearly the system's design that's the problem. They failed to implement an additional notification mechanism." Slashdot reader davidwr agrees, writing in a comment: "Proper alarms would be a hardwired alarm that would be visible or audiable to someone who was on-site who could've gotten everyone out of the water. The blame for the injuries goes to the water park and/or whatever consultant told them it was okay not to have an on-site, hardwired alarm."
Read more of this story at Slashdot.
- Apple Eyes 2027 Launch For AI-Powered Smart Glasses
Apple is reportedly targeting WWDC 2027 to unveil its first smart glasses, with shipments planned before the end of that year. According to Bloomberg's Mark Gurman (paywalled), the company has hopes of making them its flagship new product for 2027. Forbes reports: It's no secret that Meta with its Ray-Ban Meta and Oakley Meta glasses, for instance, lead the field when it comes to smart specs. "Apple is counting on integration with the apps people already use on their iPhones to be a key differentiator for the glasses," Gurman said. The App Store has millions of apps while Meta's apps are far fewer. It seems the smart glasses will use a version of the software used on the Vision Pro. "The thinking inside Apple is that while Meta has the increasingly popular Muse agent, Apple has the App Store. Because the Siri integrations are being developed for the iPhone first, software makers won't need to build separate applications for the glasses," Gurman insisted. It seems the glasses will do a lot, from making restaurant reservations to booking cars, ordering coffee or buying movie tickets. "It's also Apple's big AI monetization opportunity," Gurman believes. Part of the experience will depend on Apple's own AI agent system, it seems. There won't be augmented reality in the glasses and they will be lighter than the competition, but with longer battery life and more sensors. Gurman refers to cameras, in the plural, while current models only have one camera, or none at all in the case of Even Realities which tout their privacy aspects. "Apple is also emphasizing the sound quality," Gurman says, "which employees have said is industry-leading, with support for phone calls, music playback and FaceTime audio communication."
Read more of this story at Slashdot.
- Corporations Are Using Trump's Tariff Refunds On Bonuses Rather Than Reimbursing
An anonymous reader quotes a report from ProPublica: When Stanley Black & Decker, one of the world's largest tool companies, got hit with President Donald Trump's tariffs last year, the firm made clear that it would be sharing the pain with its customers. The Connecticut-based company raised prices again and again, moves its executives said were necessary because of the new fees on imports. Now, after the Supreme Court struck down Trump's most sweeping tariffs earlier this year, the company is getting at least $298 million refunded. Instead of sharing that bounty with its customers, however, the firm has chosen different recipients: Its own leaders. The company is one of at least nine that have disclosed that they are using their refunds not to pay back the cash-strapped consumers who generally covered much of the tariff costs through higher prices, but to give bonuses, according to a ProPublica analysis of thousands of securities filings and earnings calls for publicly traded companies. Other recognizable companies include the owners of discount department stores TJ Maxx and Marshalls and the golf equipment brand Titleist. Dozens of other firms have said little about how they plan to use the money other than to characterize the windfall as the kind of earnings they use to determine executive bonuses. The Trump administration has not publicly detailed which companies are getting the roughly $170 billion in refunds or how much they've asked for, and it has denied ProPublica's requests for this information. But reporters found some of these details while reviewing the disclosures of thousands of publicly traded companies. Some have described vague plans to pay the money forward by, for example, "returning tariff refunds to our members through pricing," though they generally don't say whether that involves price cuts or limiting future increases. Others are paying back businesses they sold products to because they had itemized receipts that detailed the tariff markups. But consumers hoping for refunds appear to be largely out of luck. With the help of artificial intelligence, ProPublica identified companies that said they planned to refund customers with their tariff windfalls. Almost all of them deal with other businesses, not consumers. "Executive bonuses are probably the least just way to use this money because it wasn't anything the executives did that they should be rewarded for. It was a government mistake that resulted in a refund," said Gregory Germain, a corporate law professor at Syracuse University. "It really explains why it's so important for the government, when they're doing something like this, to think it through to make sure consumers don't pay extra money and not get it back."
Read more of this story at Slashdot.
- SpaceX Catches Starship On the First Try
Over the weekend, SpaceX successfully caught a Starship upper stage returning from orbit for the first time, demonstrating a key piece of its plan for a fully and rapidly reusable launch system. The achievement means SpaceX has now demonstrated tower catches of both Starship stages, though not yet on the same flight. "Many small fixes are needed to achieve immediate reusability (like an airplane)," noted SpaceX's Elon Musk. The Register reports: Flight 15 began well, with the 33 Raptor engines of the Super Heavy booster launching the stack from Pad 2 at Starbase, Texas. Hot staging followed, and the booster performed its directional flip maneuver. Thirty-two Raptor engines relit for the boostback burn, intended to return Super Heavy to the tower for another catch. The booster had managed the maneuver on flight tests 5, 7, and 8, but this time something went wrong. "The boostback burn ended early due to low fuel mass," SpaceX said. The booster automatically aborted its return to the tower and diverted offshore. It completed a landing burn, briefly hovering above the Gulf before its engines shut down and the flight termination system delivered an explosive finale. Starship reached orbit under the power of its six Raptor engines and deployed 26 Starlink V3 satellites. Unlike the previous flight's brief orbital stint, this mission lasted almost a day. Following a deorbit burn, Starship returned to the launch site 22 and a half hours after it left.
Read more of this story at Slashdot.
- Robert Pattinson Named As New 007
Robert Pattinson has officially been cast as the next James Bond, succeeding Daniel Craig as 007 and ending months of speculation over actors including Callum Turner, Nicholas Hoult and Jack Lowden. Denis Villeneuve will direct the new Amazon MGM film, with Steven Knight writing the screenplay. "James Bond is one of the most legendary characters in cinema, and to be entrusted with 007 is the honor of a lifetime," Pattinson said in a statement. "I'm deeply grateful to Denis, Amy, David, Tanya and everyone at Amazon MGM Studios for their belief in me. To say this role is a dream come true is an understatement. I couldn't be more excited about this partnership and the work ahead with this fantastic team." Variety reports: Pattinson picks up the 007 mantle after Daniel Craig's five-movie run as the womanizing super spy, which began in 2006 with "Casino Royale." Craig's final turn was in 2021's "No Time to Die," which ends with Bond sacrificing himself to save the world from a secret global terrorist organization. "No Time to Die" was also the last film in the series released before longtime producers Michael G. Wilson and Barbara Broccoli sold creative control of the franchise to Amazon MGM for $20 million. [...] Pattinson also has the big IP experience needed to lead a franchise like James Bond. In 2022, Pattinson debuted as the titular Caped Crusader in Matt Reeves' "The Batman." He is set to revisit Gotham for the sequel in 2028. Those doubting Pattinson would land 007 often pointed to his obligations to Bruce Wayne as a reason why he could never take on Bond. However, after several production delays with "The Batman Part II," it seems Pattinson is ready for a new longterm relationship with another familiar big-screen icon.
Read more of this story at Slashdot.
- From DHCP to SZTP – The Trust Revolution
By Juha Holkkola, FusionLayer Group The Dawn of Effortless Connectivity In the transformative years of the late 1990s, a quiet revolution took place, fundamentally altering how we connect to networks. The introduction of DHCP answered a crucial question, Where are you on the network?!, by automating IP address assignment. This innovation eradicated the manual configuration [0]
The post From DHCP to SZTP – The Trust Revolution appeared first on Linux.com.
- MRDIMM 8800 MT/s vs. 12800 MT/s Memory Performance With AMD EPYC Venice
With last week9s AMD EPYC 9006 SP7 availability and the AMD EPYC 9686F and EPYC 9996 processor reviews, one of the most frequent questions/comments was around the impact that the new MRDIMM-12800 memory had on these Zen 6 server processors compared to prior gen and the Intel/NVIDIA server competition. Given that curiosity over the MRDIMM-12800 impact, here are the EPYC 9686F 2P benchmarks when re-testing at 8800 MT/s memory speeds.
- Rust Nightly To Begin Enabling Parallel Frontend By Default
While Rust's back-end has long been using multiple threads for compiling code, the Rust front-end has been executing sequentially by default. Finally, Rust Nightly is in the process of beginning to enable its parallel front-end by default to allow for more testing ahead of its eventual stabilization...
- GCC 17 Might Land Native AArch64 Darwin/macOS Support
After being in development since the GCC 10 days (2020) and already patched in the GCC compiler builds for Homebrew and MacPorts, the upstream GCC 17 compiler might finally land native AArch64 Darwin support for benefiting macOS with Apple Silicon...
- Modern NTFS Driver Gaining O_TMPFILE Support With Linux 7.5
The modern NTFS Linux driver that was introduced with the "NTFS Resurrection" back in Linux 7.2 continues seeing new features enabled and other improvements made to this open-source NTFS read/write kernel driver. For the upcoming Linux 7.5 kernel cycle, O_TMPFILE support is being queued for temporary file handling...
- Finally, a truly premium Linux laptop: Star Labs� StarFighter Ultra
Many popular Linux laptops are not designed from the ground-up for Linux. Often, they are machines designed and assembled by companies like Clevo, with parts and options picked by the Linux OEM to optimise them for Linux to make sure the hardware is optimally compatible. While there�s nothing wrong with this approach � there are countless great Linux laptops available that are made this way � there�s also something to be said for starting with a blank slate, and designing, developing, building, and assembling a Linux laptop entirely from scratch. One such laptop is Star Labs� brand new StarFighter, which I�ve been using and testing over the last little while since it was launched. The StarFighter is an entirely custom powerhouse of a laptop, designed exclusively for Linux, both inside and out. Let�s talk about what it�s like to use the StarFighter, and if it�s worth considering when looking for a new laptop. The hardware The Starfighter comes in three flavours: Standard, Ultra, and AMD. I opted for the Ultra model, which comes with an Intel Core Ultra 9 285H, an Intel Arc 140T integrated GPU, 64GB of LPDDR5X RAM, and a 16C 3840×2400 120Hz matte display. The standard model steps these specs down to an Intel Core Ultra 5 125H, 32GB of LPDDR5X RAM, and a 16C 2560×1600 165Hz display, while the AMD model maintains the specifications of the Ultra, but with an AMD Ryzen 7 8845HS processor paired with a Radeon 780M integrated GPU. All three models share the same Intel AX210 Wi-Fi 6E chip, soldered RAM, and port configuration: 2 USB-C ports (Thunderbolt 4 on the Intel models), 3 USB-A ports, an HDMI 2.0 port, a microSD reader, a combined audio jack, and two PCIe Gen 4 NVMe slots on the motherboard. All three models run coreboot firmware, and come with a hardware kill switch for the wireless radios. Another really interesting security and privacy feature is how the Starfighter handles its webcam. Instead of being integrated into the display bezel, the webcam is a separate module that snaps onto the display lid magnetically, connecting through a few pogo pins (which form a USB 2.0 port, which I�m sure intrepid hardware hackers could do fun stuff with). When not in use, the webcam module is stored in its own little metal tray that slides out of the side of the laptop, securing itself in place magnetically. Neat. The webcam quality itself is decidedly average. I personally don�t ever use a webcam, but if you do, don�t expect miracles. It does its job, no more, no less. The StarFighter has a custom chassis made out of magnesium, with the only plastic part of the casing being the display inner hinge cover where I assume the antennas are integrated. It�s an incredibly sturdy device, with very little flex in the display cover, and zero flex in the keyboard deck. Thanks to the properties of magnesium, it�s quite lightweight at a mere 1.6kg. The bottom cover is easily removable, but the two screws in the middle of that cover are ever so slightly longer than all the other screws � ask me how I know. Star Labs opted for an understated, unobtrusive design. There�s no weird flourishes, no garish RGB lighting, no childish font on the keyboard � it�s all business, and I really like that. The dark finish feels incredibly nice, and despite the colour doesn�t seem to catch too many fingerprints. The speaker grills next to the keyboard look nice too, as does the keyboard itself � I especially appreciate that the the various modifier and non-character keys use text labels instead of symbols. Of course, since this is a Linux laptop, the super key is properly labelled. No Windows logo here, but no silly penguin either. The keyboard is backlit, of course, with several light levels, with a keyboard backlight timeout adjustable in coreboot. Using it The feel of the keyboard could use some work, however, at least for me. In particular, the key stability feels a bit off to me, meaning that unless you strike a key right in the middle, it might not register properly, as the keys wobble more than I would expect. A workaround, of sorts, is to strike the keys a bit harder than you normally would, but I�ve found this to be more difficult to adapt to than I initially expected. That being said, if you already have a more solid strike, it�s possible you won�t notice anything wrong with the keyboard at all. The trackpad, though, is basically perfect. Star Labs pulled out all the stops here, and went for a large haptic trackpad that feels absolutely incredible. I greatly prefer haptic trackpads, and have been puzzled for years now why Linux laptop OEMs continue to opt for wobbly diving board-style trackpads instead. It has a glass surface which hits the perfect middle-ground between smooth and textured, and it never seems to pick up any smudges or grease. Several of the parameters of the haptic trackpad can be configured in coreboot and supposedly from within Linux itself, but I haven�t figured that part out yet as the patches for it were only accepted very recently. It is the perfect trackpad. Zero complaints. Every single click, every single gesture, every single swoosh feels perfect. I don�t like being this ecstatic about something � there�s usually flaws in everything � but it�s really just that good. While testing the StarFighter, I used some other laptops with the old diving board design, and they�re all ruined for me now. I�m usually a fan of smaller laptops, with 14C being my upper bound. However, laptops have gotten so light, and bezels so thin, that the 16C of today is the 14C of several years ago � not exactly, but you get my point. I definitely had to get used to this larger laptop, but now that I have acclimatised, having 3840×2400 pixels spread out across a 16C canvas is honestly kind of amazing. I
- KDE will now load XWayland on demand
When running KDE, the X11 compatibility layer for Wayland, XWayland, always runs, even if there isn�t anything on the system still requiring the legacy X server to work. In the next step towards a Wayland-only world, the KDE people have reached a major milestone: XWayland now only runs when actually needed. This week a significant technical milestone was achieved: the XWayland compatibility layer is now loaded only when needed. Previously it had always been running even when no apps were using it, and fixing this required porting various system services away from legacy X11 code paths. This work was done by Vlad Zahorodnii, David Edmundson, and David Redondo, and will ship in Plasma 6.9. ↫ Nate Graham This frees up some system resources, which is always a welcome improvement. I do wonder how this might impact the load times of legacy X applications, but I have a feeling it�s close to immeasurable.
- Redox gets Go, GIMP, and more
I love and admire the Redox project, but their insistence on fudging the publication dates of their monthly progress reports really bothers me, for some reason. No, I�m not 16 days late � the report covering October was published only yesterday evening, and not on 31 October as the website claims. None of this matters to anyone but weird people such as myself, but I still want to get it off my chest. Don�t bother any Redox people about this. Anyway, the big news for the month of October is the port of the official Go programming language compiler, allowing for cross-compilation and self-hosted compilation using relibc. Another major port also made its way to Redox in October: GIMP now runs on Redox, using the Orbital backend of the GTK port. The work to make Redox compatible with Cloud Hypervisor is also complete, with more information in its own dedicated article. Video playback in WebKitGTK3 has been fixed as well, and even YouTube works now which is quite neat. There�s a ton more in this report, like an updated Servo port, NUMA support has been tested on real hardware for the first time and seems to work, work on rootless package installation has begun, and much more.
- Disk encryption on NetBSD: achieving secrecy
NetBSD developer Nia Alarie has written a guide on how to set up a NetBSD system with disk encryption that�s quite useful for those of us who deeply care about such a level of security. On top of that, the guide is also interesting if you just want to learn a bit more about how NetBSD works. The guide is written for sparc64, but should work on more mainstream architectures just as well. A guide written by a NetBSD developer is obviously going to employ some exotic or weird hardware. As is tradition.
- Creating a self-booting ZIP archive
Linux initramfs supports unpacking CPIO, a stupid, simple, standardized format. In the discussion on whether to support TAR instead, much emphasize has been put on the fact that CPIO is standardized and less fragmented. Luckily, Linux (the kernel) includes its own tool to produce the specific variant of the standard that it happens to implement. The standard CPIO tool is possibly the most cursed archiver under the SUN. In the old DOS/WinDOS world, ZIP was probably the most widespread and well-known archive format, being displaced to some extent by the rise of RAR during the 2000s. Because of the design of the format, ZIP lends itself to all kinds of polyglot trickery. Way back when, self extracting ZIP archives where a thing, EXE/ZIP polyglots that can be run and unpack themselves, which is useful if you don�t have an archiver installed. I don�t think I need to explain where I am going with this. ↫ David Oberhollenzer This is lovingly cursed.
- MenuetOS keeps steadily improving
MenuetOS, the operating system written in x86-64 assembly, has seen a few new releases since we last looked at it, delivering some welcome improvements. Secure network connections are now faster, there�s a TrueType font demo, and, of course, the usual bugfixes and smaller improvements. The game Wizord EXL100 has been ported, and a few drivers have been improved as well. You can get the latest releases from the downloads page.
- ReactOS makes strides in SMP, 64bit, and more
The ReactOS project organised two hackfests this year, and the work done during those in-person sessions, combined with the ongoing regular progress, has led to some pretty significant breakthroughs and progress. More NT6+ syscalls have been added, ReactOS supports floppy disks now, NTFS support has been vastly improved, and much more. There�s also a new USB3/4 stack, which is now merged and offers basic support for these versions of USB. One of the biggest additions is a new kernel shim engine which gives ReactOS the ability to work around buggy drivers and implement quirks, moreso than even Windows itself can. For instance, thanks to this new shim, XP-era NVIDIA drivers can run on NT6 ReactOS. The ongoing efforts to implement SMP are yielding results too: ReactOS can now run with SMP for days on end while doing tasks in the background, which is quite promising. The team is showing off Steam and the game Among Us running on ReactOS, which is definitely impressive.
- Polo: a new Wayland compositor for MATE
MATE is probably the last X11-only holdout among the major desktop environments, but that�s about to change if Kerem Söke has anything to say about it. Polo is a port of Marco�s behavior and window management policies to Wayland, built on libweston and written in Vala and C. It�s a window manager, compositor, and session authority for the MATE Wayland desktop. It takes over, step by step, what Marco, mate-session-manager and the compositor-facing parts of mate-settings-daemon do on X11. ↫ Polo�s GitHub page Söke is looking for testers with this very first Polo 1.0.0 release � cute name, too � which is available on its GitHub page.
- IBM to offer access to a dual-processor quantum system in 2027
Ars Technica published a short write-up about changes to IBM�s quantum computing plans. The changes greatly expand the scope of its next-generation Nighthawk general-use processors by adding a version with over 500 programmable qubits. At the same time, it’s stepping back a bit on its plan to link multiple Nighthawk processors together, dropping the intended number of linked systems from nine to two. The total number of qubits planned for next year will remain the same; how the company is getting there, however, will be different. Meanwhile, the company is touting the performance boost achieved via a major change that was made in the generation of Nighthawk processors released in September: hardware-based qubit resets. ↫ John Timmer at Ars Technica I�m convinced quantum computing will eventually have a big impact in the areas its characteristics are presumed to be well-suited for. Also, it just looks and sounds incredibly cool, even if as the technology currently stands it�s not particularly useful yet.
- I�m not descending into madness because mount and unmount icons make no sense
There are many problems in this world � some big, some small, some so minute nobody ought to put them to paper at all. The problem I�m going to highlight here is even smaller than that. This literally � the actual literally � does not matter and absolutely nobody should care about it, let alone put any work into changing it or addressing it some other way. I want to talk about the iconography GNOME�s Disks utility uses to symbolise mount! and unmount!. No, I�m not descending into madness. GNOME�s Disks utility uses the play! symbol on the mount button, and the stop! symbol on the unmount button. Inexplicably, considering the state of the world in general and the rapidly deteriorating quality of software specifically, this bothers me. Out in the real world, built on decades of consistent use, these symbols have gained clearly defined meanings, and mounting and unmounting disks definitely isn�t one of them. In fact, the meaning of these symbols isn�t mere convention; they�re defined in a variety of international standards for symbols for use in software and on equipment, such as ISO/IEC 18035 (which you need to buy to read; my copy fell of a truck): ISO/IEC 18035:2002 defines a consistent set of icons and related functions that are represented by multimedia applications on a computer screen and that users interact with to control such applications. It describes controls applying to such functions as: Play, Pause, Stop, Rewind, Scan forward, Scan backward, Replay backward, Loop, Go to beginning, Go to previous, Go to next, Go to end, Set volume and Mute. ↫ ISO/IEC 18035:2003 They�re also part of ISO 7000/IEC 60417, a much larger, more encompassing standard that also contains things like the various symbols used on laundry machines, tumble dryers, in cars, and so on. The symbols themselves are much older than the standards, of course, with many of them dating back to the 1960s and possibly even 1950s. The point remains, though: the play and stop symbols have clearly defined meanings, and I don�t think they are at all a good fit for mount and unmount. The function of the play! symbol according to ISO/IEC 18035: To enable the user to start the presentation of dynamic media, except where the task requires automatic playing of that media. ↫ ISO/IEC 18035:2003 And of the stop! symbol: To enable the user to stop the presentation of dynamic media. ↫ ISO/IEC 18035:2003 Neither of these descriptions match what mounting and unmounting mean or do. Mounting a drive or partition doesn�t present any media at all; it merely makes the drive or partition in question accessible. Unmounting also doesn�t eject anything; it merely makes the drive or partition inaccessible. I would argue that play and pause act upon contents of a drive or volume, and not upon the drive or volume itself. As it stands right now, you play! a drive! to play! a video stored on said drive. Madness. I already know what you�re thinking, and yes, I agree that the Disks utility is a tool aimed at more advanced use cases and users, and most normal, average users will never even know it exists, let alone open it at all. Very few people get to see these symbols, and those that do already know full well what mounting and unmounting mean, reducing the importance of said symbols considerably. But now it�s time for the big surprise, the twist in the story that turns this entire thing on its head. Files, GNOME�s file manager, uses an entirely different symbol for unmounting! Instead of the stop! symbol, Files uses the eject! symbol. You may think this is a more accurate visual representation of what unmounting means, but I strongly disagree. Let�s turn to ISO/IEC 18035:2003 once again: To enable the user to eject the current physical media from the appropriate drive. ↫ ISO/IEC 18035:2003 Unmounting doesn�t eject anything! If you unmount a USB stick, the stick doesn�t get fired out of the USB port. If you unmount a volume, it doesn�t get removed from the SSD. Hell, if you unmount a CD-ROM, it doesn�t even eject it! Ejecting a CD-ROM � opening the drive�s tray or spitting the CD-ROM out of a slot-loader � is an entirely different act! Are we really ejecting! a CD-ROM twice? Are we mounting! a CD-ROM when we merely close the tray? No! Madness! The real underlying problem here is, of course, that mounting and unmounting are deeply weird and confusing concepts, bordering on the esoteric, that simply do not have physical equivalents to fall back on. Using symbols and iconography designed in the 1960s explicitly for playing music or stopping a video or ejecting a cassette tape are not a good fit for something as difficult to explain to most people as mounting and unmounting. It�s like putting an eject symbol on a car�s door handle or a play symbol on a soap dispenser. Should GNOME developers waste any time or resources to address this? No, of course not, that would be stupid. Nobody should care about this but me. I should suffer in silence, every time I need to mount or unmount something, forced to look for an eject or stop symbol in whatever user interface I happen to be using. Every time, I should die a little inside. Please, don�t be like me and waste precious resources thinking about this. I�m not descending into madness. I just want mount and unmount symbols that make sense. I�m not descending into madness.
- EU OS: A Bold Step Toward Digital Sovereignty for Europe
Image 
A new initiative, called "EU OS," has been launched to develop a Linux-based operating system tailored specifically for the public sector organizations of the European Union (EU). This community-driven project aims to address the EU's unique needs and challenges, focusing on fostering digital sovereignty, reducing dependency on external vendors, and building a secure, self-sufficient digital ecosystem.
What Is EU OS?
EU OS is not an entirely novel operating system. Instead, it builds upon a Linux foundation derived from Fedora, with the KDE Plasma desktop environment. It draws inspiration from previous efforts such as France's GendBuntu and Munich's LiMux, which aimed to provide Linux-based systems for public sector use. The goal remains the same: to create a standardized Linux distribution that can be adapted to different regional, national, and sector-specific needs within the EU.
Rather than reinventing the wheel, EU OS focuses on standardization, offering a solid Linux foundation that can be customized according to the unique requirements of various organizations. This approach makes EU OS a practical choice for the public sector, ensuring broad compatibility and ease of implementation across diverse environments.
The Vision Behind EU OS
The guiding principle of EU OS is the concept of "public money – public code," ensuring that taxpayer money is used transparently and effectively. By adopting an open-source model, EU OS eliminates licensing fees, which not only lowers costs but also reduces the dependency on a select group of software vendors. This provides the EU’s public sector organizations with greater flexibility and control over their IT infrastructure, free from the constraints of vendor lock-in.
Additionally, EU OS offers flexibility in terms of software migration and hardware upgrades. Organizations can adapt to new technologies and manage their IT evolution at a manageable cost, both in terms of finances and time.
However, there are some concerns about the choice of Fedora as the base for EU OS. While Fedora is a solid and reliable distribution, it is backed by the United States-based Red Hat. Some argue that using European-backed projects such as openSUSE or KDE's upcoming distribution might have aligned better with the EU's goal of strengthening digital sovereignty.
Conclusion
EU OS marks a significant step towards Europe's digital independence by providing a robust, standardized Linux distribution for the public sector. By reducing reliance on proprietary software and vendors, it paves the way for a more flexible, cost-effective, and secure digital ecosystem. While the choice of Fedora as the base for the project has raised some questions, the overall vision of EU OS offers a promising future for Europe's public sector in the digital age.
Source: It's FOSS
European Union
- Linus Torvalds Acknowledges Missed Release of Linux 6.14 Due to Oversight
Linus Torvalds Acknowledges Missed Release of Linux 6.14 Due to Oversight
Linux kernel lead developer Linus Torvalds has admitted to forgetting to release version 6.14, attributing the oversight to his own lapse in memory. Torvalds is known for releasing new Linux kernel candidates and final versions on Sunday afternoons, typically accompanied by a post detailing the release. If he is unavailable due to travel or other commitments, he usually informs the community ahead of time, so users don’t worry if there’s a delay.
In his post on March 16, Torvalds gave no indication that the release might be delayed, instead stating, “I expect to release the final 6.14 next weekend unless something very surprising happens.” However, Sunday, March 23rd passed without any announcement.
On March 24th, Torvalds wrote in a follow-up message, “I’d love to have some good excuse for why I didn’t do the 6.14 release yesterday on my regular Sunday afternoon schedule,” adding, “But no. It’s just pure incompetence.” He further explained that while he had been clearing up unrelated tasks, he simply forgot to finalize the release. “D'oh,” he joked.
Despite this minor delay, Torvalds’ track record of successfully managing the Linux kernel’s development process over the years remains strong. A single day’s delay is not critical, especially since most Linux users don't urgently need the very latest version.
The new 6.14 release introduces several important features, including enhanced support for writing drivers in Rust—an ongoing topic of discussion among developers—support for Qualcomm’s Snapdragon 8 Elite mobile chip, a fix for the GhostWrite vulnerability in certain RISC-V processors from Alibaba’s T-Head Semiconductor, and a completed NTSYNC driver update that improves the WINE emulator’s ability to run Windows applications, particularly games, on Linux.
Although the 6.14 release went smoothly aside from the delay, Torvalds expressed that version 6.15 may present more challenges due to the volume of pending pull requests. “Judging by my pending pile of pull requests, 6.15 will be much busier,” he noted.
You can download the latest kernel here.
Linus Torvalds kernel
- AerynOS 2025.03 Alpha Released with GNOME 48, Mesa 25, and Linux Kernel 6.13.8
Image 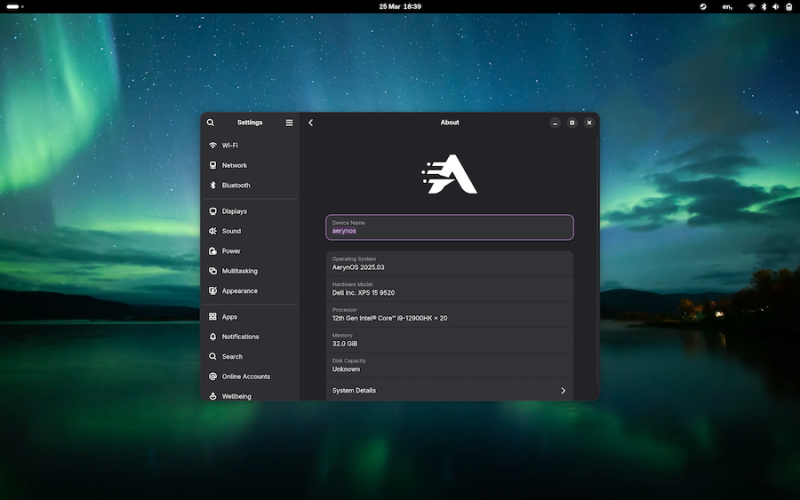
AerynOS 2025.03 has officially been released, introducing a variety of exciting features for Linux users. The release includes the highly anticipated GNOME 48 desktop environment, which comes with significant improvements like HDR support, dynamic triple buffering, and a Wayland color management protocol. Other updates include a battery charge limiting feature and a Wellbeing option aimed at improving user experience.
This release, while still in alpha, incorporates Linux kernel 6.13.8 and the updated Mesa 25.0.2 graphics stack, alongside tools like LLVM 19.1.7 and Vulkan SDK 1.4.309.0. Additionally, the Moss package manager now integrates os-info to generate more detailed OS metadata via a JSON file.
Future plans for AerynOS include automated package updates, easier rollback management, improved disk handling with Rust, and fractional scaling enabled by default. The installer has also been revamped to support full disk wipes and dynamic partitioning.
Although still considered an alpha release, AerynOS 2025.03 can be downloaded and tested right now from its official website.
Source: 9to5Linux
AerynOS
- Xojo 2025r1: Big Updates for Developers with Linux ARM Support, Web Drag and Drop, and Direct App Store Publishing
Image 
Xojo has just rolled out its latest release, Xojo 2025 Release 1, and it’s packed with features that developers have been eagerly waiting for. This major update introduces support for running Xojo on Linux ARM, including Raspberry Pi, brings drag-and-drop functionality to the Web framework, and simplifies app deployment with the ability to directly submit apps to the macOS and iOS App Stores.
Here’s a quick overview of what’s new in Xojo 2025r1:
1. Linux ARM IDE Support
Xojo 2025r1 now allows developers to run the Xojo IDE on Linux ARM devices, including popular platforms like Raspberry Pi. This opens up a whole new world of possibilities for developers who want to create apps for ARM-based devices without the usual complexity. Whether you’re building for a Raspberry Pi or other ARM devices, this update makes it easier than ever to get started.
2. Web Drag and Drop
One of the standout features in this release is the addition of drag-and-drop support for web applications. Now, developers can easily drag and drop visual controls in their web projects, making it simpler to create interactive, user-friendly web applications. Plus, the WebListBox has been enhanced with support for editable cells, checkboxes, and row reordering via dragging. No JavaScript required!
3. Direct App Store Publishing
Xojo has also streamlined the process of publishing apps. With this update, developers can now directly submit macOS and iOS apps to App Store Connect right from the Xojo IDE. This eliminates the need for multiple steps and makes it much easier to get apps into the App Store, saving valuable time during the development process.
4. New Desktop and Mobile Features
This release isn’t just about web and Linux updates. Xojo 2025r1 brings some great improvements for desktop and mobile apps as well. On the desktop side, all projects now include a default window menu for macOS apps. On the mobile side, Xojo has introduced new features for Android and iOS, including support for ColorGroup and Dark Mode on Android, and a new MobileColorPicker for iOS to simplify color selection.
5. Performance and IDE Enhancements
Xojo’s IDE has also been improved in several key areas. There’s now an option to hide toolbar captions, and the toolbar has been made smaller on Windows. The IDE on Windows and Linux now features modern Bootstrap icons, and the Documentation window toolbar is more compact. In the code editor, developers can now quickly navigate to variable declarations with a simple Cmd/Ctrl + Double-click. Plus, performance for complex container layouts in the Layout Editor has been enhanced.
What Does This Mean for Developers?
Xojo 2025r1 brings significant improvements across all the platforms that Xojo supports, from desktop and mobile to web and Linux. The added Linux ARM support opens up new opportunities for Raspberry Pi and ARM-based device development, while the drag-and-drop functionality for web projects will make it easier to create modern, interactive web apps. The ability to publish directly to the App Store is a game-changer for macOS and iOS developers, reducing the friction of app distribution.
How to Get Started
Xojo is free for learning and development, as well as for building apps for Linux and Raspberry Pi. If you’re ready to dive into cross-platform development, paid licenses start at $99 for a single-platform desktop license, and $399 for cross-platform desktop, mobile, or web development. For professional developers who need additional resources and support, Xojo Pro and Pro Plus licenses start at $799. You can also find special pricing for educators and students.
Download Xojo 2025r1 today at xojo.com.
Final Thoughts
With each new release, Xojo continues to make cross-platform development more accessible and efficient. The 2025r1 release is no exception, delivering key updates that simplify the development process and open up new possibilities for developers working on a variety of platforms. Whether you’re a Raspberry Pi enthusiast or a mobile app developer, Xojo 2025r1 has something for you.
Xojo ARM
- New 'Mirrored' Network Mode Introduced in Windows Subsystem for Linux
Microsoft's Windows Subsystem for Linux (WSL) continues to evolve with the release of WSL 2 version 0.0.2. This update introduces a set of opt-in preview features designed to enhance performance and compatibility.
Key additions include "Automatic memory reclaim" which dynamically optimizes WSL's memory footprint, and "Sparse VHD" to shrink the size of the virtual hard disk file. These improvements aim to streamline resource usage.
Additionally, a new "mirrored networking mode" brings expanded networking capabilities like IPv6 and multicast support. Microsoft claims this will improve VPN and LAN connectivity from both the Windows host and Linux guest.
Complementing this is a new "DNS Tunneling" feature that changes how DNS queries are resolved to avoid compatibility issues with certain network setups. According to Microsoft, this should reduce problems connecting to the internet or local network resources within WSL.
Advanced firewall configuration options are also now available through Hyper-V integration. The new "autoProxy" feature ensures WSL seamlessly utilizes the Windows system proxy configuration.
Microsoft states these features are currently rolling out to Windows Insiders running Windows 11 22H2 Build 22621.2359 or later. They remain opt-in previews to allow testing before final integration into WSL.
By expanding WSL 2 with compelling new capabilities in areas like resource efficiency, networking, and security, Microsoft aims to make Linux on Windows more performant and compatible. This evolutionary approach based on user feedback highlights Microsoft's commitment to WSL as a key part of the Windows ecosystem.
Windows
- Linux Threat Report: Earth Lusca Deploys Novel SprySOCKS Backdoor in Attacks on Government Entities
The threat actor Earth Lusca, linked to Chinese state-sponsored hacking groups, has been observed utilizing a new Linux backdoor dubbed SprySOCKS to target government organizations globally.
As initially reported in January 2022 by Trend Micro, Earth Lusca has been active since at least 2021 conducting cyber espionage campaigns against public and private sector targets in Asia, Australia, Europe, and North America. Their tactics include spear-phishing and watering hole attacks to gain initial access. Some of Earth Lusca's activities overlap with another Chinese threat cluster known as RedHotel.
In new research, Trend Micro reveals Earth Lusca remains highly active, even expanding operations in the first half of 2023. Primary victims are government departments focused on foreign affairs, technology, and telecommunications. Attacks concentrate in Southeast Asia, Central Asia, and the Balkans regions.
After breaching internet-facing systems by exploiting flaws in Fortinet, GitLab, Microsoft Exchange, Telerik UI, and Zimbra software, Earth Lusca uses web shells and Cobalt Strike to move laterally. Their goal is exfiltrating documents and credentials, while also installing additional backdoors like ShadowPad and Winnti for long-term spying.
The Command and Control server delivering Cobalt Strike was also found hosting SprySOCKS - an advanced backdoor not previously publicly reported. With roots in the Windows malware Trochilus, SprySOCKS contains reconnaissance, remote shell, proxy, and file operation capabilities. It communicates over TCP mimicking patterns used by a Windows trojan called RedLeaves, itself built on Trochilus.
At least two SprySOCKS versions have been identified, indicating ongoing development. This novel Linux backdoor deployed by Earth Lusca highlights the increasing sophistication of Chinese state-sponsored threats. Robust patching, access controls, monitoring for unusual activities, and other proactive defenses remain essential to counter this advanced malware.
The Trend Micro researchers emphasize that organizations must minimize attack surfaces, regularly update systems, and ensure robust security hygiene to interrupt the tactics, techniques, and procedures of relentless threat groups like Earth Lusca.
Security
- Linux Kernel Faces Reduction in Long-Term Support Due to Maintenance Challenges
The Linux kernel is undergoing major changes that will shape its future development and adoption, according to Jonathan Corbet, Linux kernel developer and executive editor of Linux Weekly News. Speaking at the Open Source Summit Europe, Corbet provided an update on the latest Linux kernel developments and a glimpse of what's to come.
A major change on the horizon is a reduction in long-term support (LTS) for kernel versions from six years to just two years. Corbet explained that maintaining old kernel branches indefinitely is unsustainable and most users have migrated to newer versions, so there's little point in continuing six years of support. While some may grumble about shortened support lifecycles, the reality is that constantly backporting fixes to ancient kernels strains maintainers.
This maintainer burnout poses a serious threat, as Corbet highlighted. Maintaining Linux is largely a volunteer effort, with only about 200 of the 2,000+ developers paid for their contributions. The endless demands on maintainers' time from fuzz testing, fixing minor bugs, and reviewing contributions takes a toll. Prominent maintainers have warned they need help to avoid collapse. Companies relying on Linux must realize giving back financially is in their interest to sustain this vital ecosystem.
The Linux kernel is also wading into waters new with the introduction of Rust code. While Rust solves many problems, it also introduces new complexities around language integration, evolving standards, and maintainer expertise. Corbet believes Rust will pass the point of no return when core features depend on it, which may occur soon with additions like Apple M1 GPU drivers. Despite skepticism in some corners, Rust's benefits likely outweigh any transition costs.
On the distro front, Red Hat's decision to restrict RHEL cloning sparked community backlash. While business considerations were at play, Corbet noted technical factors too. Using older kernels with backported fixes, as RHEL does, risks creating divergent, vendor-specific branches. The Android model of tracking mainline kernel dev more closely has shown security benefits. Ultimately, Linux works best when aligned with the broader community.
In closing, Corbet recalled the saying "Linux is free like a puppy is free." Using open source seems easy at first, but sustaining it long-term requires significant care and feeding. As Linux is incorporated into more critical systems, that maintenance becomes ever more crucial. The kernel changes ahead are aimed at keeping Linux healthy and vibrant for the next generation of users, businesses, and developers.
kernel
- Linux Celebrates 32 Years with the Release of 6.6-rc2 Version
Today marks the 32nd anniversary of Linus Torvalds introducing the inaugural Linux 0.01 kernel version, and celebrating this milestone, Torvalds has launched the Linux 6.6-rc2. Among the noteworthy updates are the inclusion of a feature catering to the ASUS ROG Flow X16 tablet's mode handling and the renaming of the new GenPD subsystem to pmdomain.
The Linux 6.6 edition is progressing well, brimming with exciting new features that promise to enhance user experience. Early benchmarks are indicating promising results, especially on high-core-count servers, pointing to a potentially robust and efficient update in the Linux series.
Here is what Linus Torvalds had to say in today's announcement:
Another week, another -rc.I think the most notable thing about 6.6-rc2 is simply that it'sexactly 32 years to the day since the 0.01 release. And that's a roundnumber if you are a computer person.Because other than the random date, I don't see anything that reallystands out here. We've got random fixes all over, and none of it looksparticularly strange. The genpd -> pmdomain rename shows up in thediffstat, but there's no actual code changes involved (make sure touse "git diff -M" to see them as zero-line renames).And other than that, things look very normal. Sure, the architecturefixes happen to be mostly parisc this week, which isn't exactly theusual pattern, but it's also not exactly a huge amount of changes.Most of the (small) changes here are in drivers, with some tracingfixes and just random things. The shortlog below is short enough toscroll through and get a taste of what's been going on. Linus Torvalds
- Introducing Bavarder: A User-Friendly Linux Desktop App for Quick ChatGPT Interaction
Want to interact with ChatGPT from your Linux desktop without using a web browser?
Bavarder, a new app, allows you to do just that.
Developed with Python and GTK4/libadwaita, Bavarder offers a simple concept: pose a question to ChatGPT, receive a response, and promptly copy the answer (or your inquiry) to the clipboard for pasting elsewhere.
With an incredibly user-friendly interface, you won't require AI expertise (or a novice blogger) to comprehend it. Type your question in the top box, click the blue send button, and wait for a generated response to appear at the bottom. You can edit or modify your message and repeat the process as needed.
During our evaluation, Bavarder employed BAI Chat, a GPT-3.5/ChatGPT API-based chatbot that's free and doesn't require signups or API keys. Future app versions will incorporate support for alternative backends, such as ChatGPT 4 and Hugging Chat, and allow users to input an API key to utilize ChatGPT3.
At present, there's no option to regenerate a response (though you can resend the same question for a potentially different answer). Due to the lack of a "conversation" view, tracking a dialogue or following up on answers can be challenging — but Bavarder excels for rapid-fire questions.
As with any AI, standard disclaimers apply. Responses might seem plausible but could contain inaccurate or false information. Additionally, it's relatively easy to lead these models into irrational loops, like convincing them that 2 + 2 equals 106 — so stay alert!
Overall, Bavarder is an attractive app with a well-defined purpose. If you enjoy ChatGPT and similar technologies, it's worth exploring.
ChatGPT AI
- LibreOffice 7.5.3 Released: Third Maintenance Update Brings 119 Bug Fixes to Popular Open-Source Office Suite
Today, The Document Foundation unveiled the release and widespread availability of LibreOffice 7.5.3, which serves as the third maintenance update to the current LibreOffice 7.5 open-source and complimentary office suite series.
Approximately five weeks after the launch of LibreOffice 7.5.2, LibreOffice 7.5.3 arrives with a new set of bug fixes for those who have successfully updated their GNU/Linux system to the LibreOffice 7.5 series.
LibreOffice 7.5.3 addresses a total of 119 bugs identified by users or uncovered by LibreOffice developers. For a more comprehensive understanding of these bug fixes, consult the RC1 and RC2 changelogs.
You can download LibreOffice 7.5.3 directly from the LibreOffice website or from SourceForge as binary installers for DEB or RPM-based GNU/Linux distributions. A source tarball is also accessible for individuals who prefer to compile the software from sources or for system integrators.
All users operating the LibreOffice 7.5 office suite series should promptly update their installations to the new point release, which will soon appear in the stable software repositories of your GNU/Linux distributions.
In early February 2023, LibreOffice 7.5 debuted as a substantial upgrade to the widely-used open-source office suite, introducing numerous features and improvements. These enhancements encompass major upgrades to dark mode support, new application and MIME-type icons, a refined Single Toolbar UI, enhanced PDF Export, and more.
Seven maintenance updates will support LibreOffice 7.5 until November 30th, 2023. The next point release, LibreOffice 7.5.4, is scheduled for early June and will include additional bug fixes.
The Document Foundation once again emphasizes that the LibreOffice office suite's "Community" edition is maintained by volunteers and members of the Open Source community. For enterprise implementations, they suggest using the LibreOffice Enterprise family of applications from ecosystem partners.
LibreOffice
|